Joujik Mutualwork
The GRC audit workspace where your evidence never leaves your Drive.
8 frameworks · 692 controls — ISO 27001 · SOC 2 · GDPR · Israeli Privacy Law · AI · cloud · privacy — run real compliance engagements while every file stays in the customer's own Google Drive.
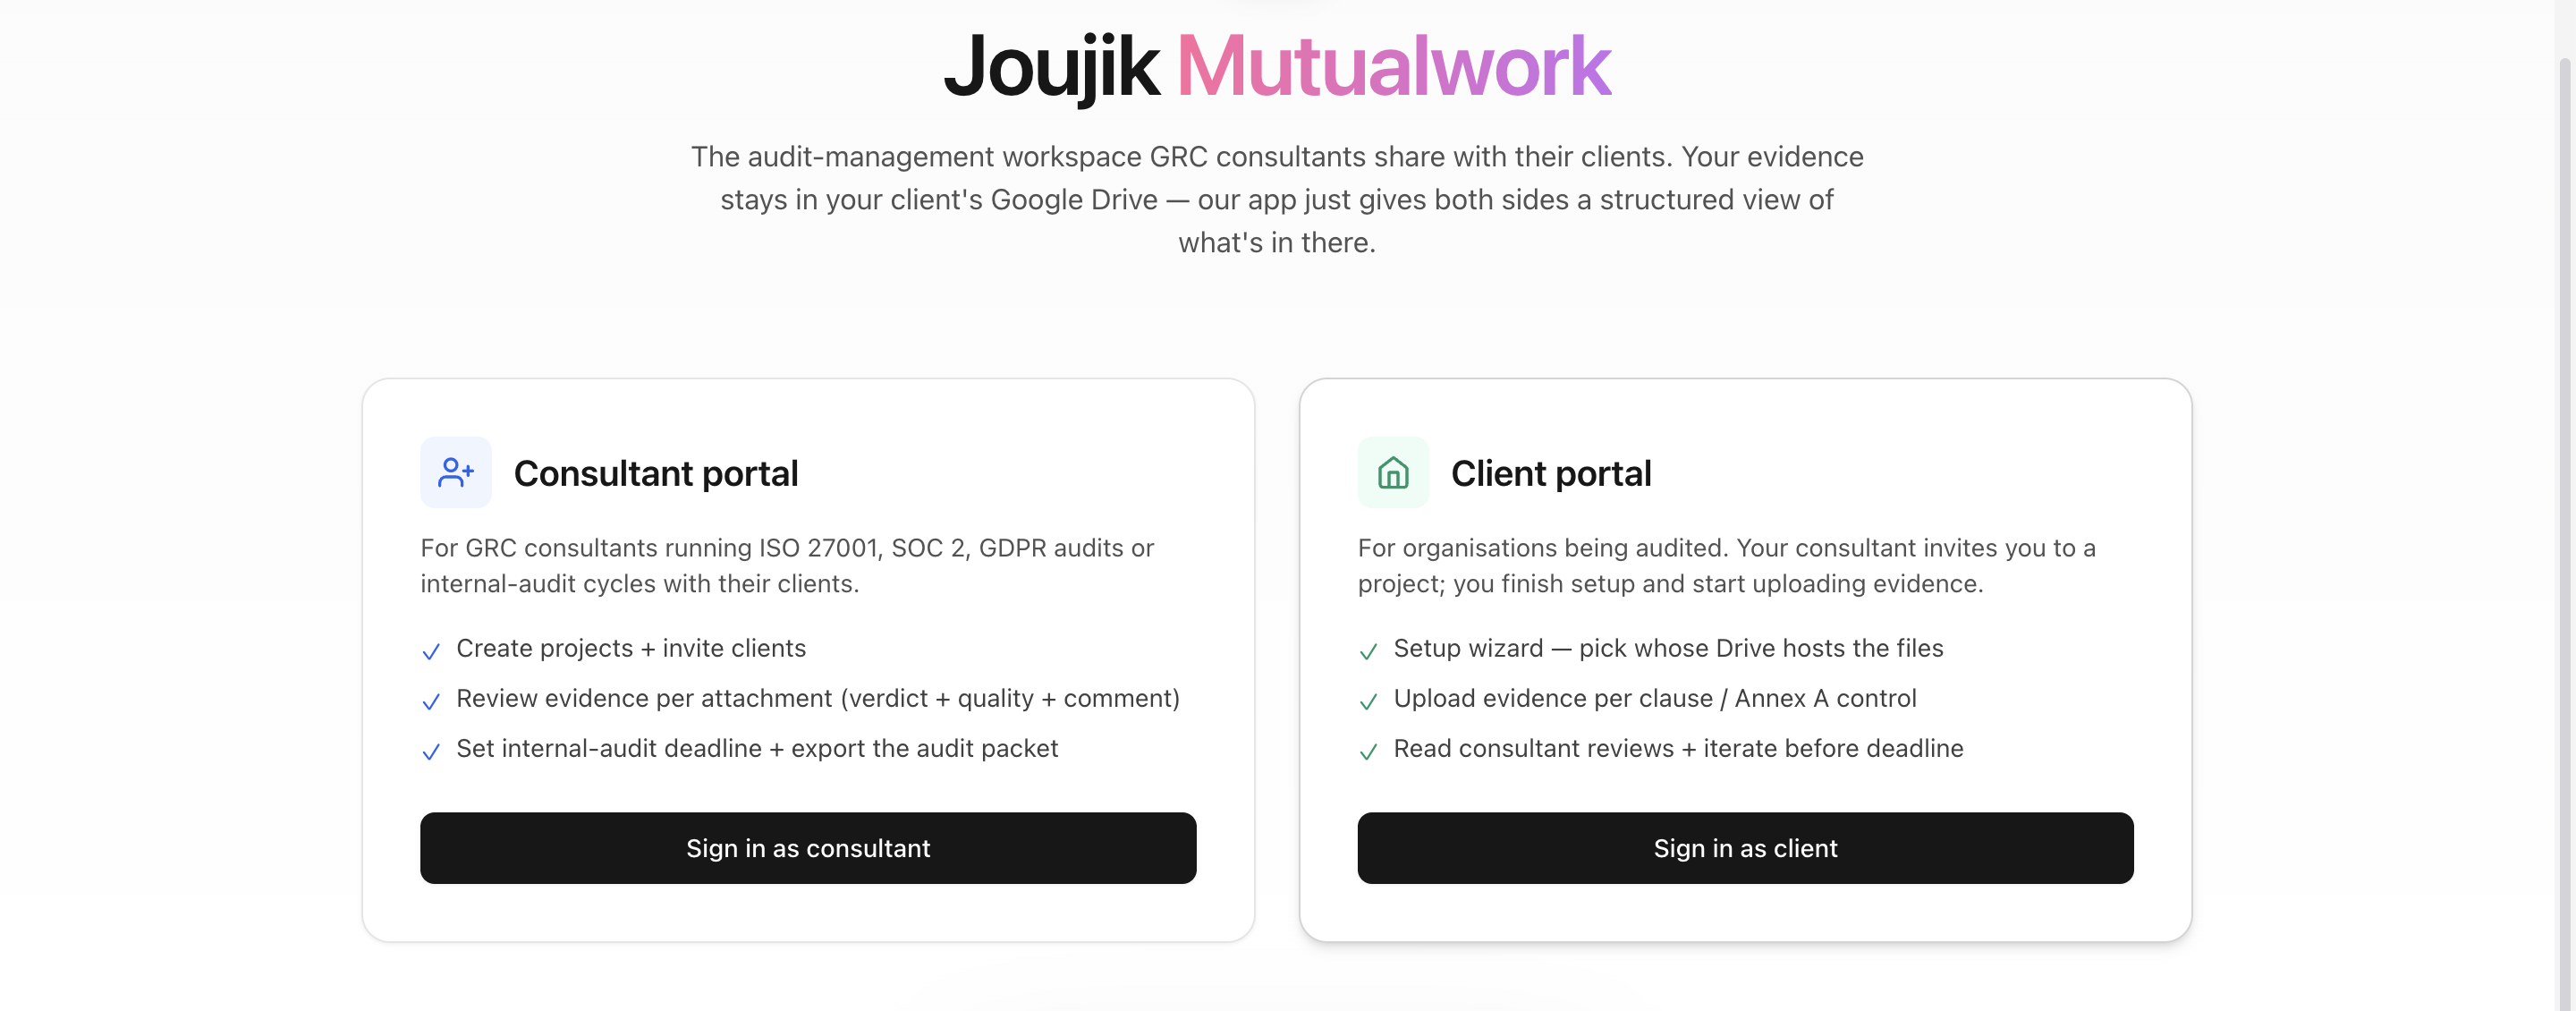
Invite-only, two-sided.
Two clear portals — consultant and client. Access is by approval (private beta), and either side can own the Drive folder — the owner keeps the evidence, even if the other party changes.
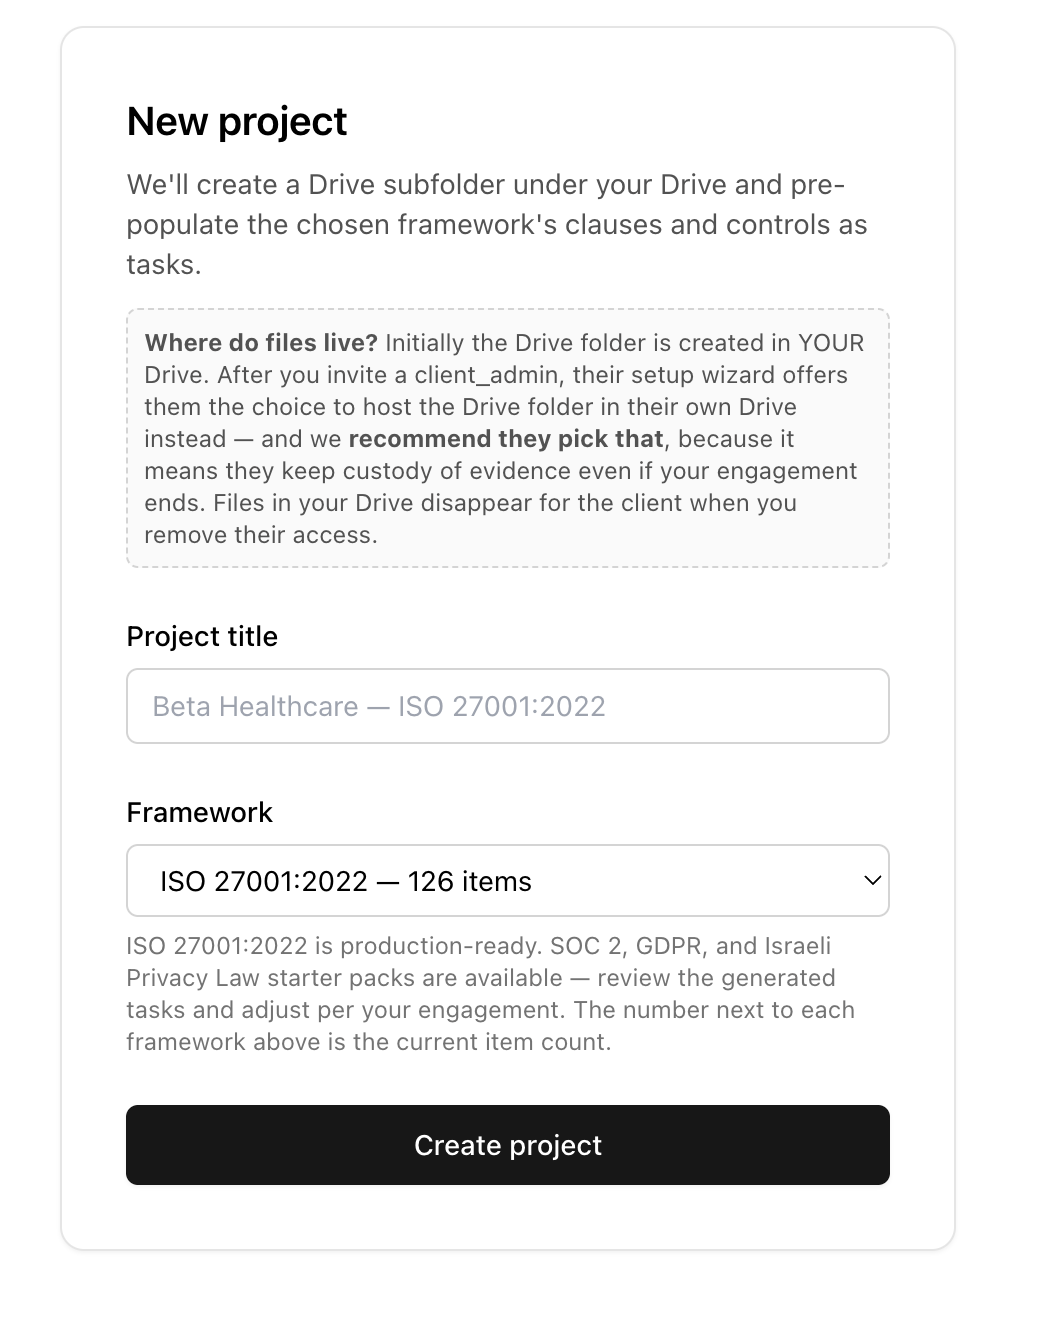
Pick a framework.
Choose one of eight frameworks. Pick ISO 27001:2022 and the engagement spins up a Drive folder and materialises the 93 Annex A controls + clauses 4–10 as 126 audit tasks — ready for evidence.
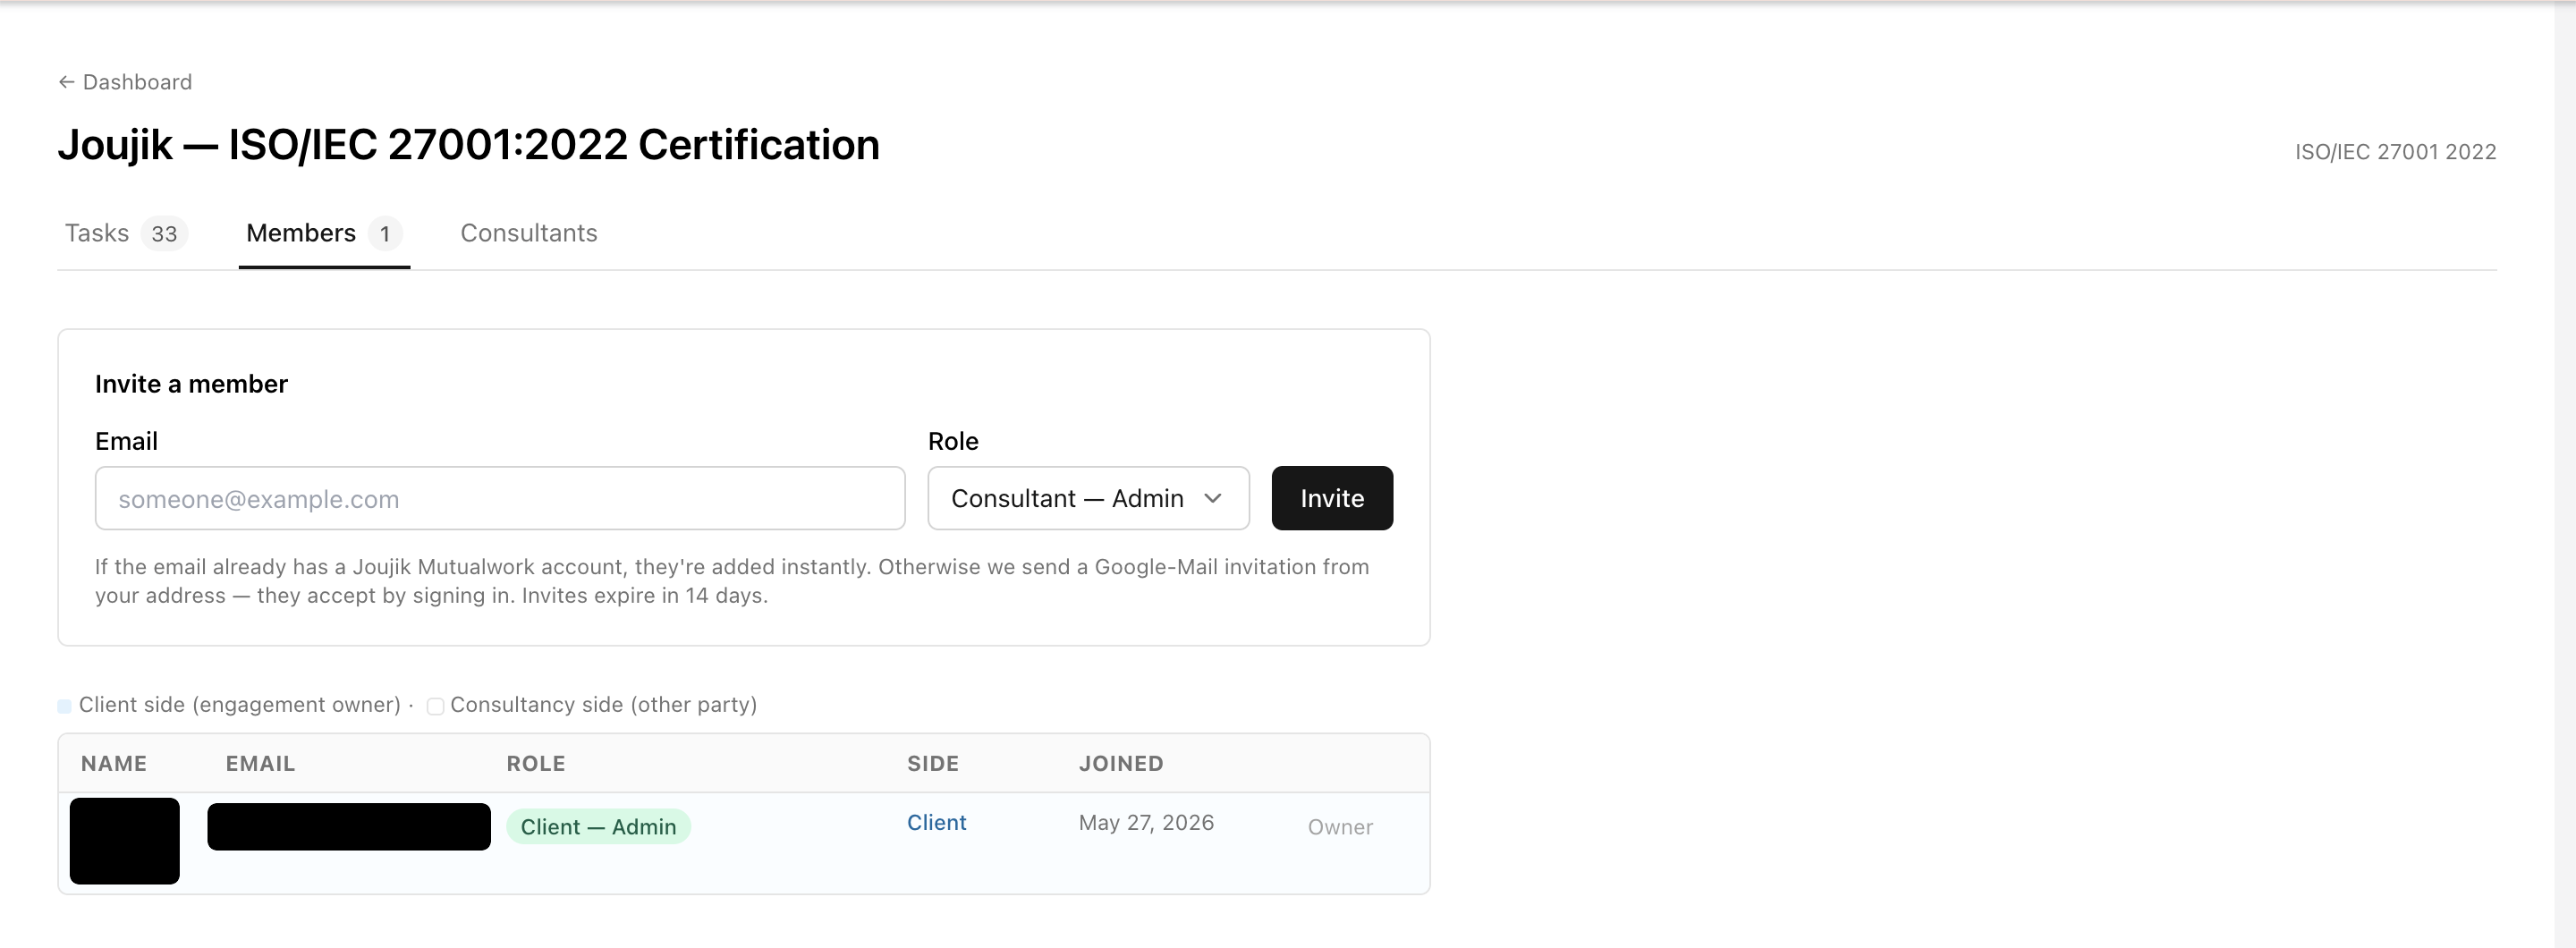
Bring in the other side.
The engagement owner invites the counterpart by email with a role. Client side and consultancy side are tracked separately — with a live, shared member list.
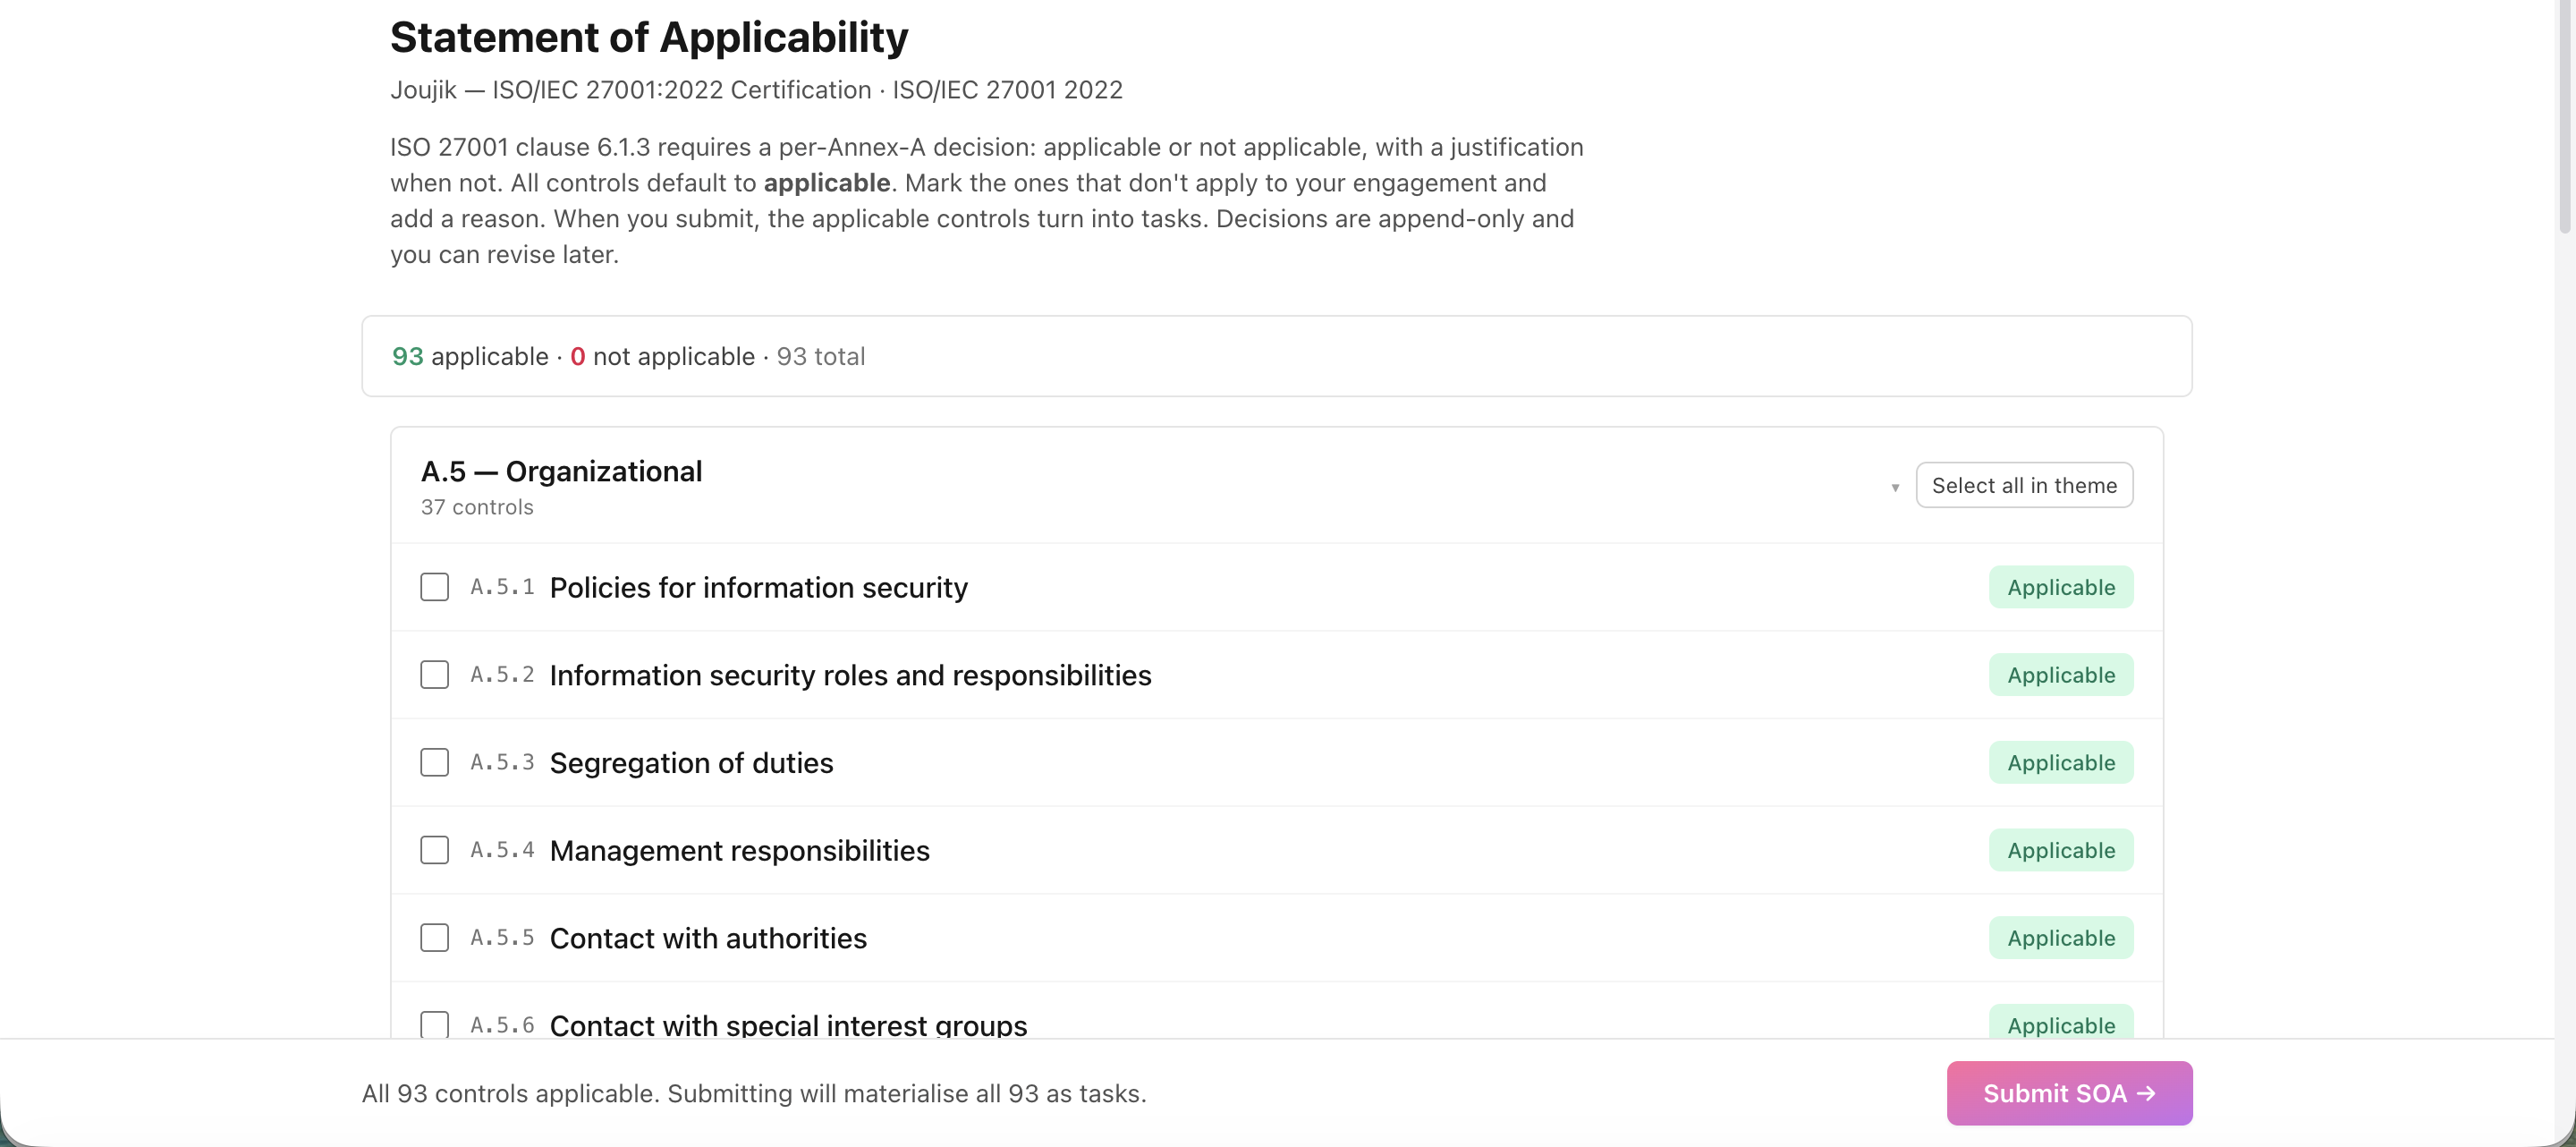
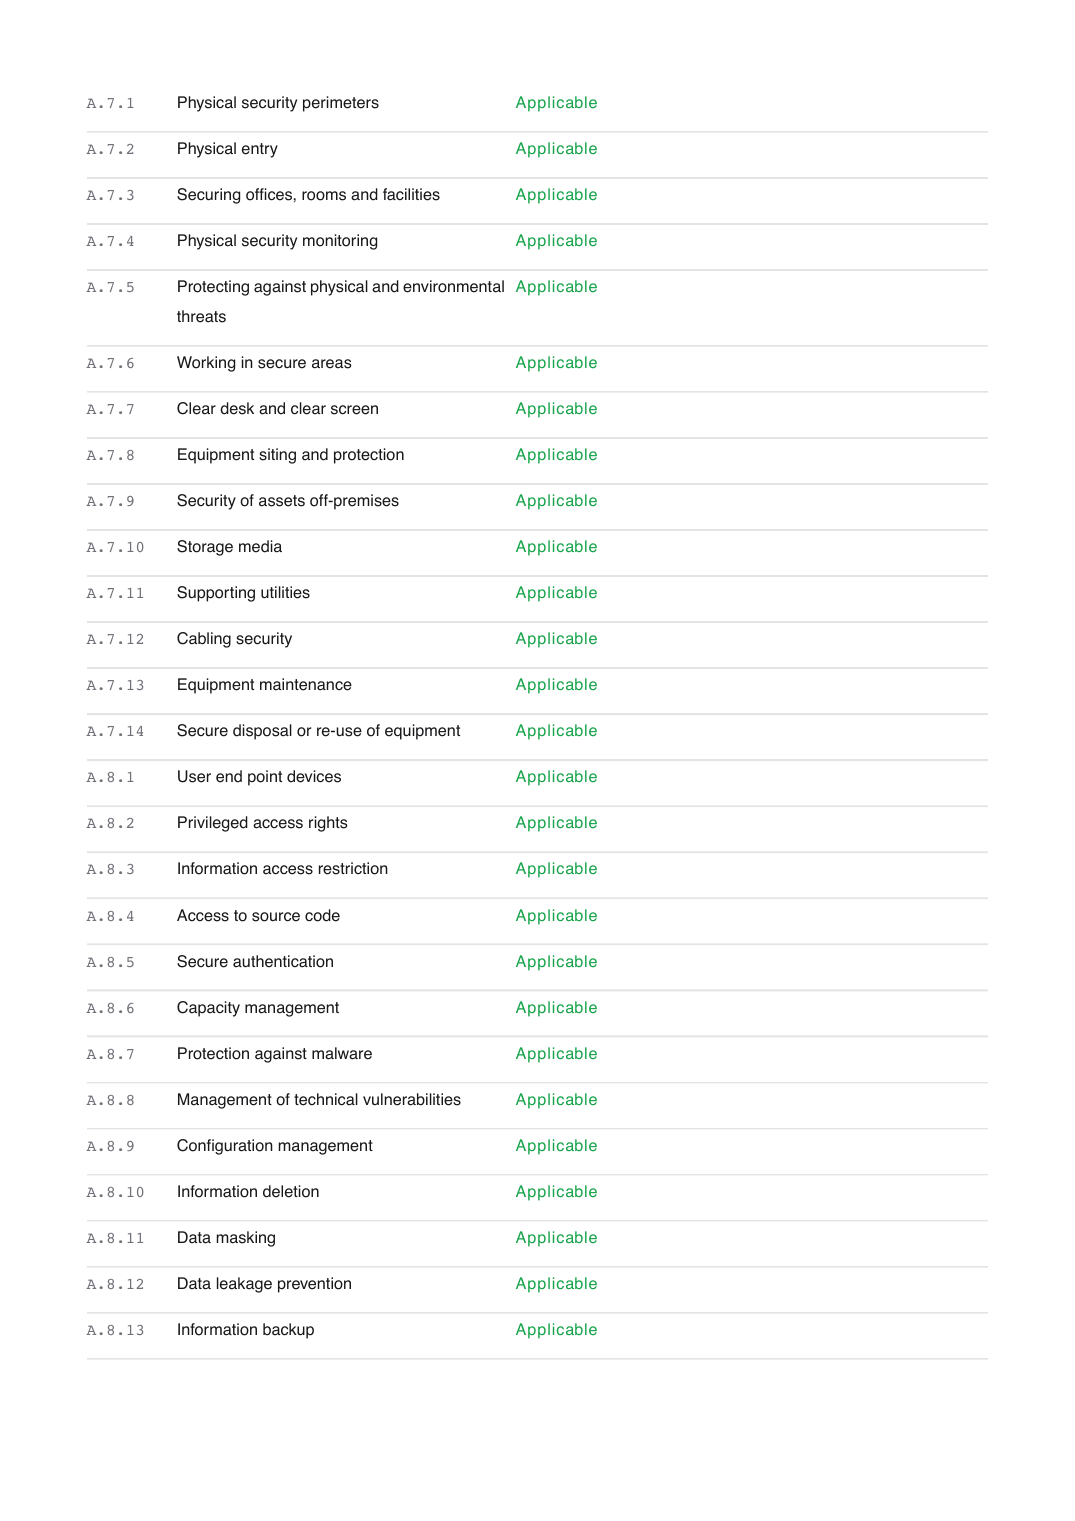
The Statement of Applicability.
Mark each of the 93 Annex A controls applicable or excluded — with a justification (per clause 6.1.3). Submit, and the applicable controls become live tasks.
Upload, then the auditor verdicts it.
The client uploads evidence (straight to Drive); the consultant runs an internal-audit review of each control — comply, OFI or non-conformity — with a quality tag and a comment to the client.
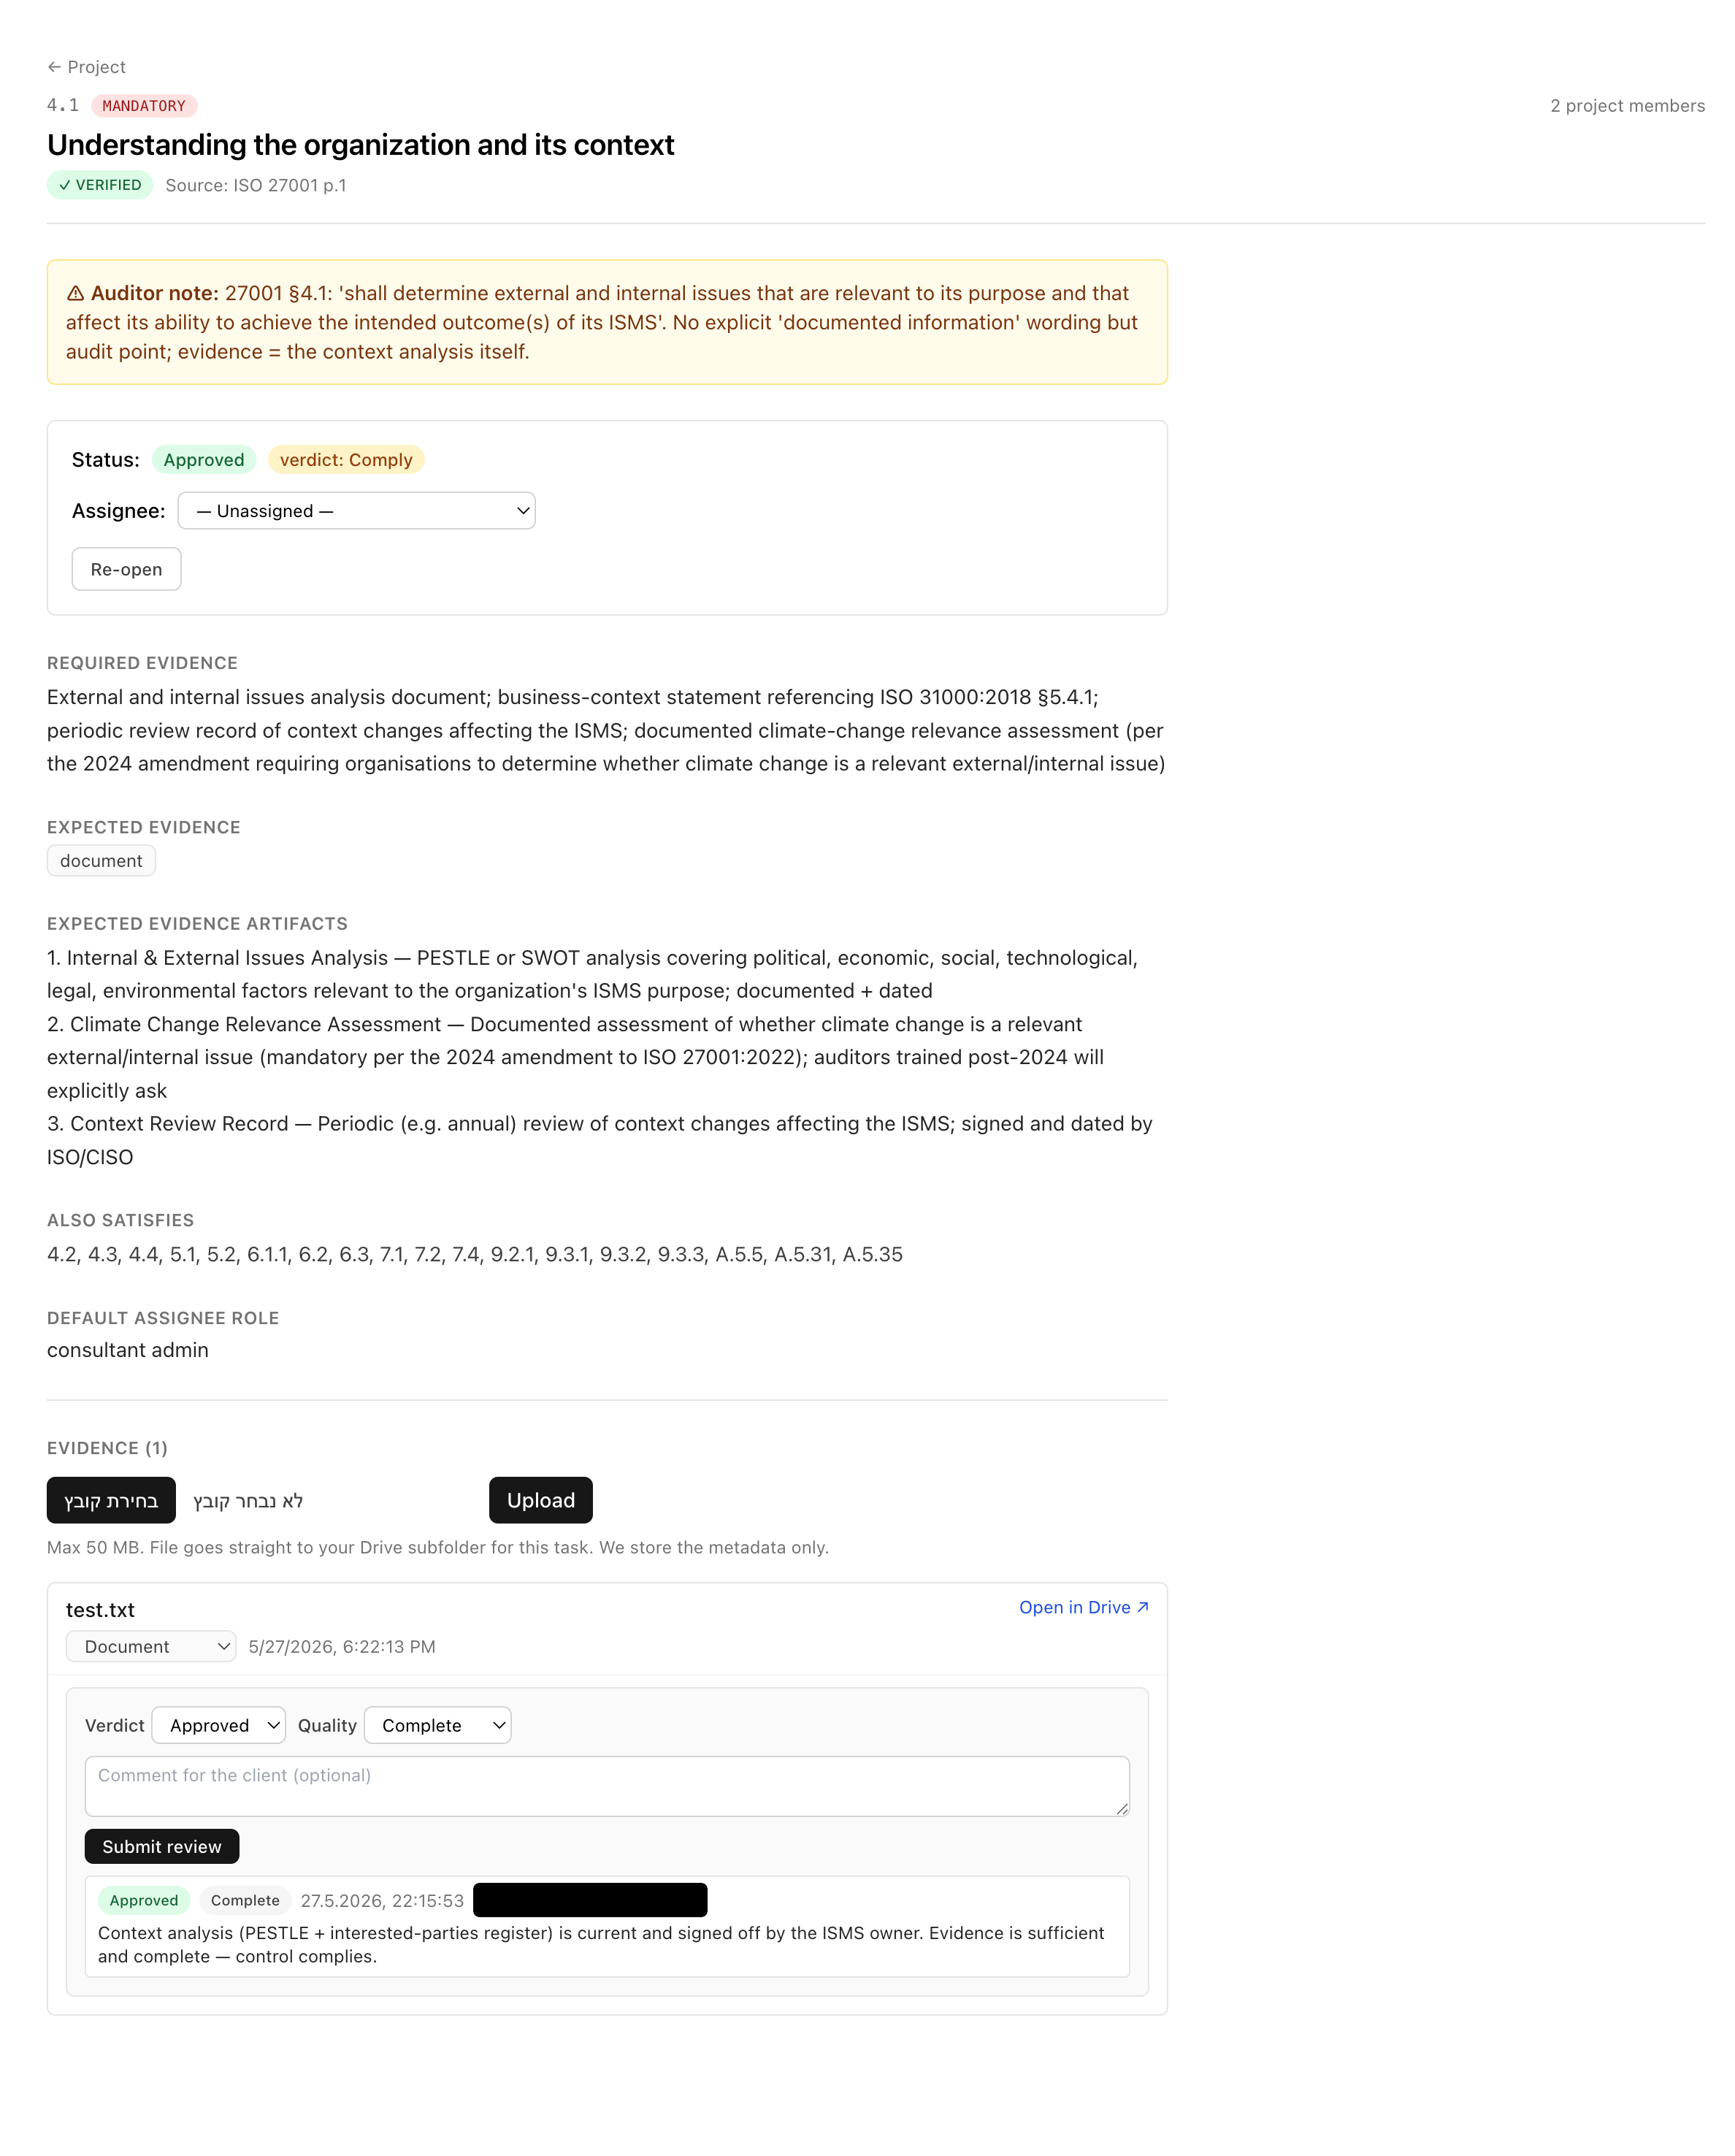
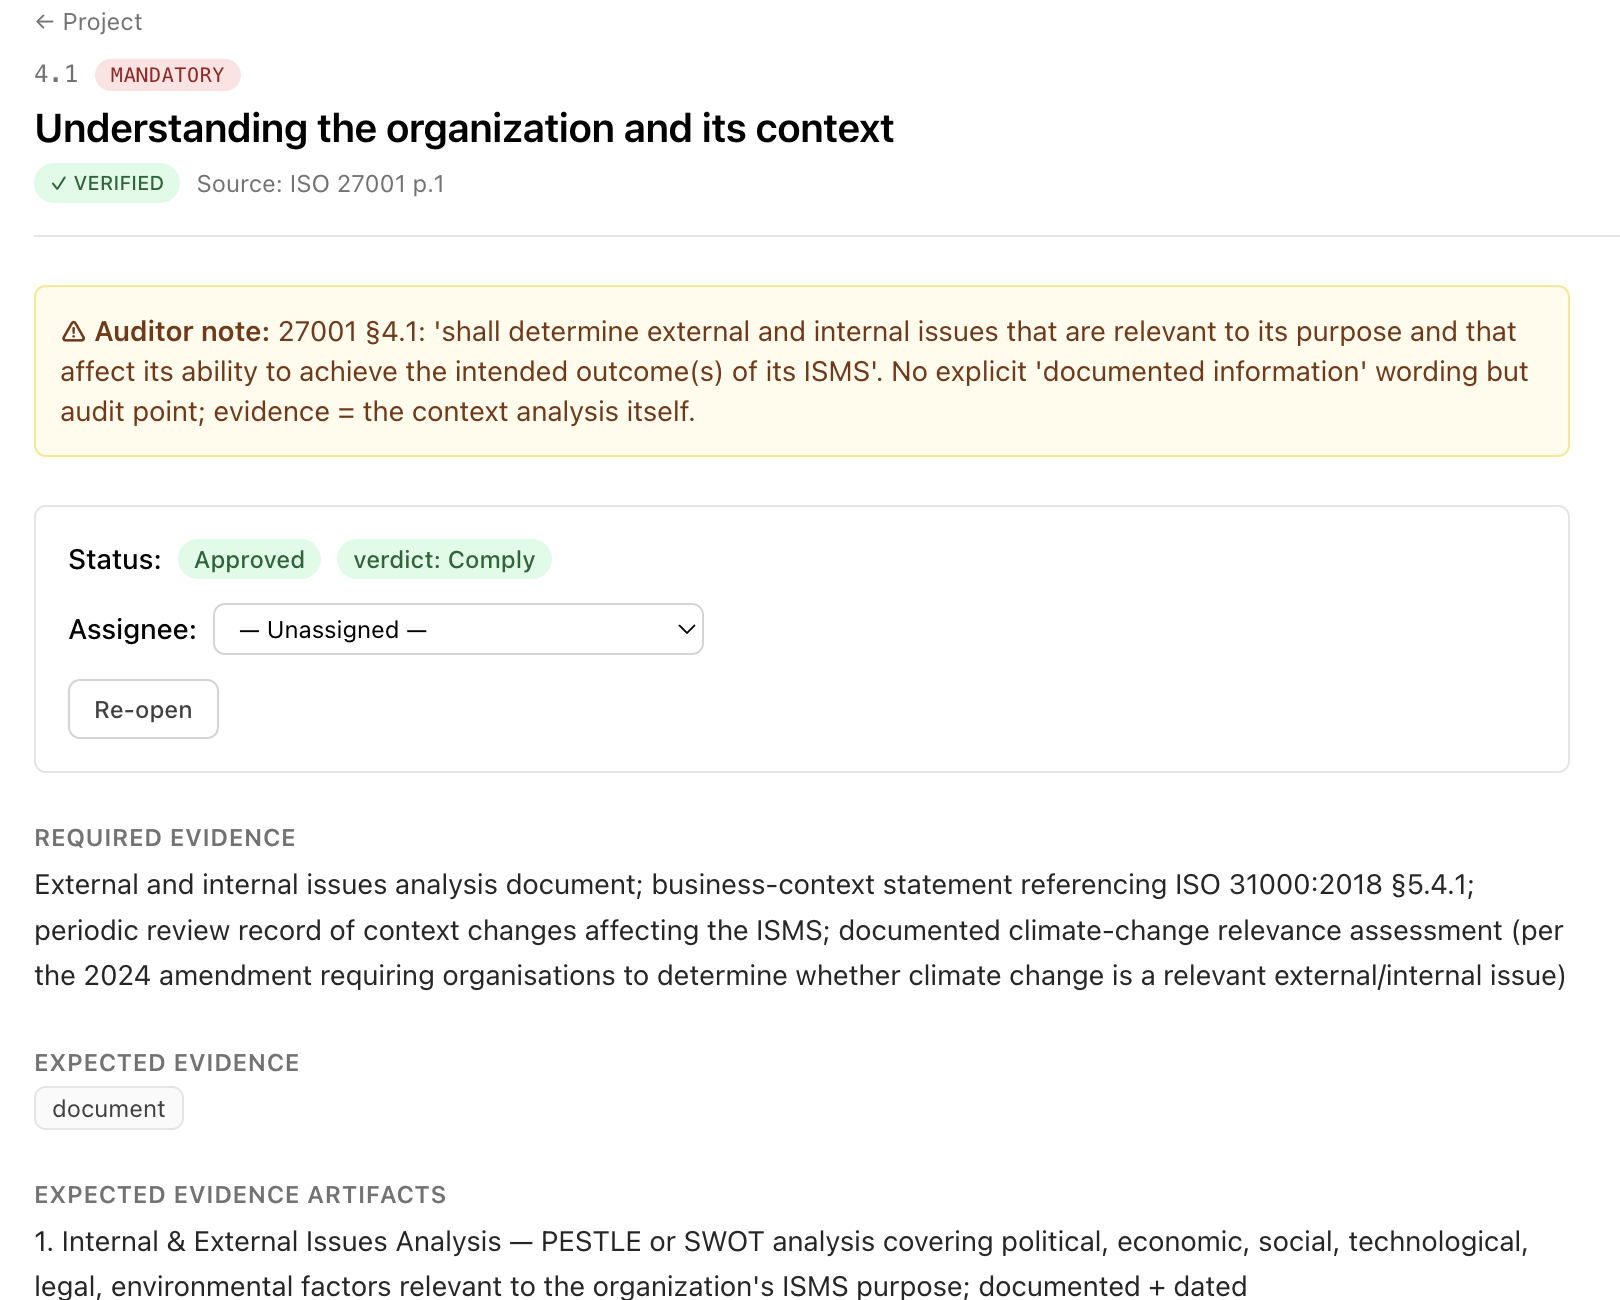
The client knows exactly what the auditor expects.
Every control ships with an auditor note, required evidence and
expected artifacts — down to the exact file name the auditor looks for
(e.g. ISMS_Scope_Document.docx). 611 controls covered today. No guessing, fewer rejected uploads.
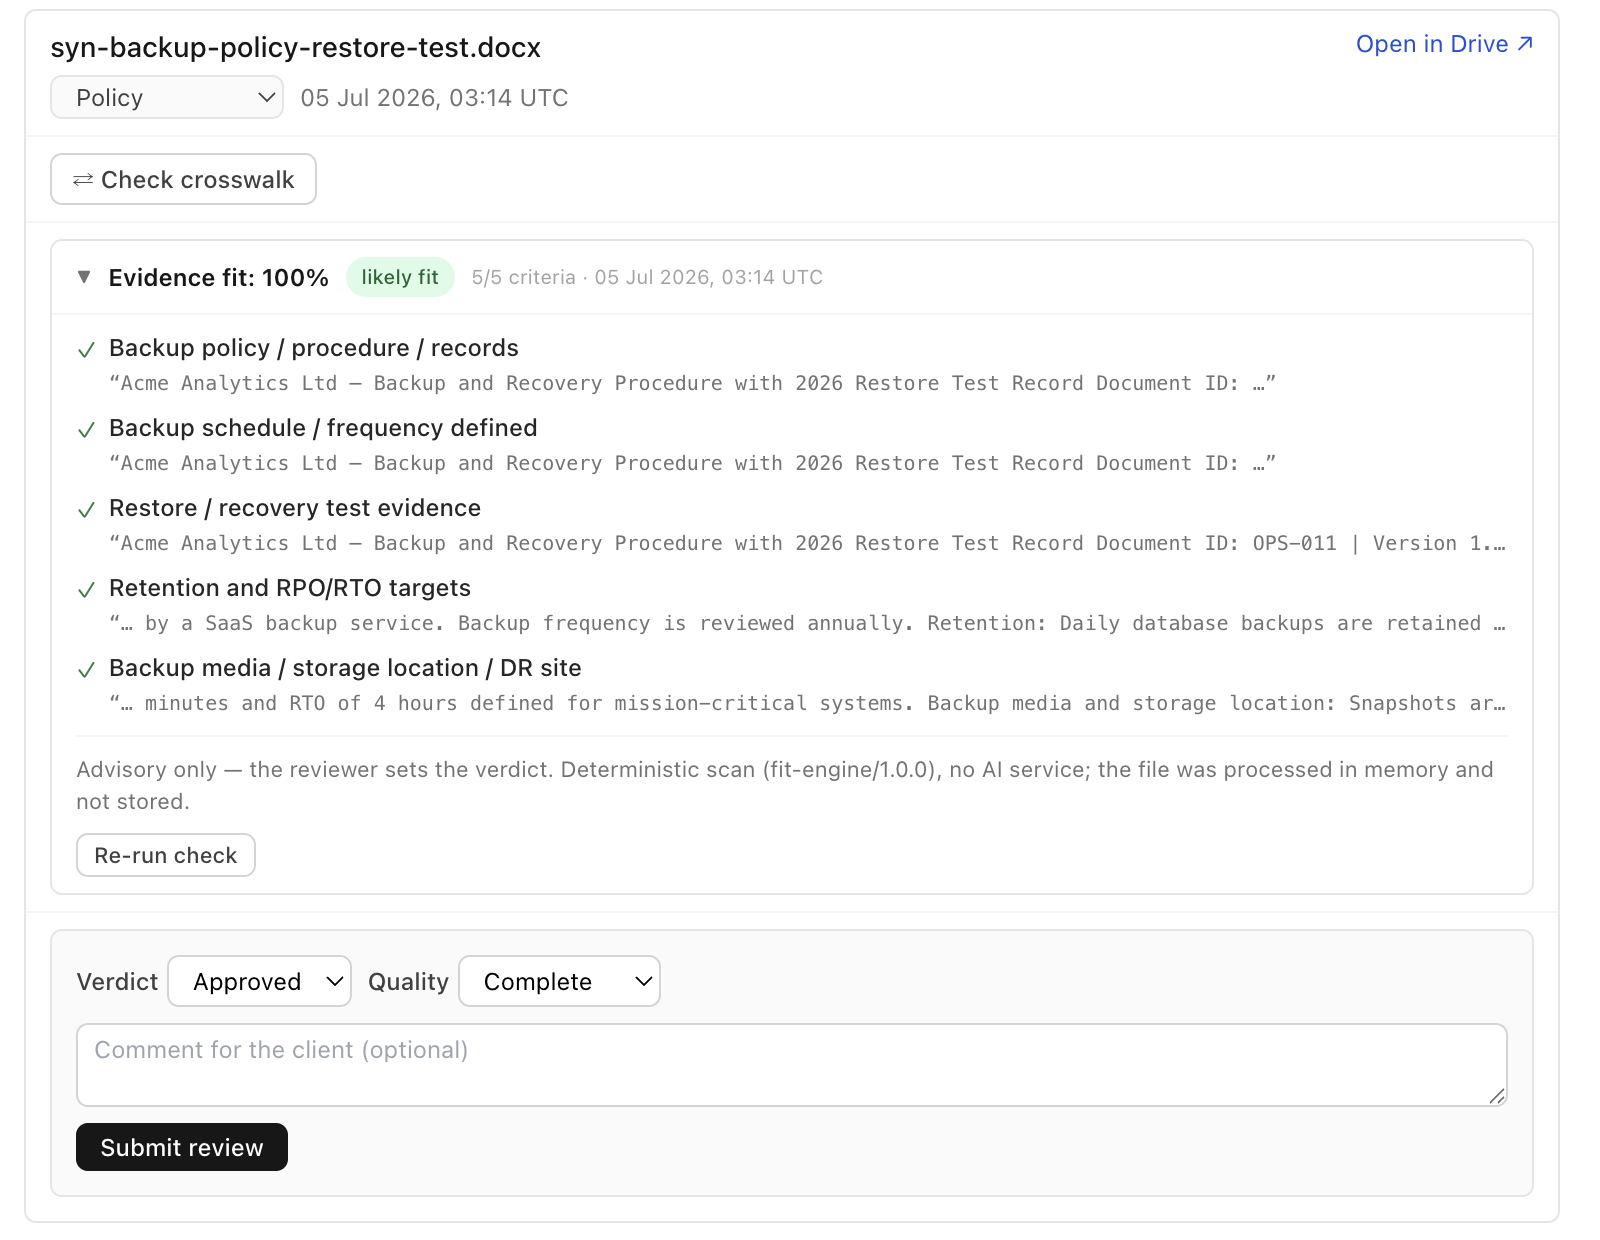
Every upload is pre-checked. Deterministically.
A rules-based engine — no AI, no LLM — reads the file in memory and checks it against the control's auditor criteria: "5/5 criteria matched" with quoted snippets, or a list of what's missing. Only the result is stored, never the file. 94.4% accuracy on our benchmark.
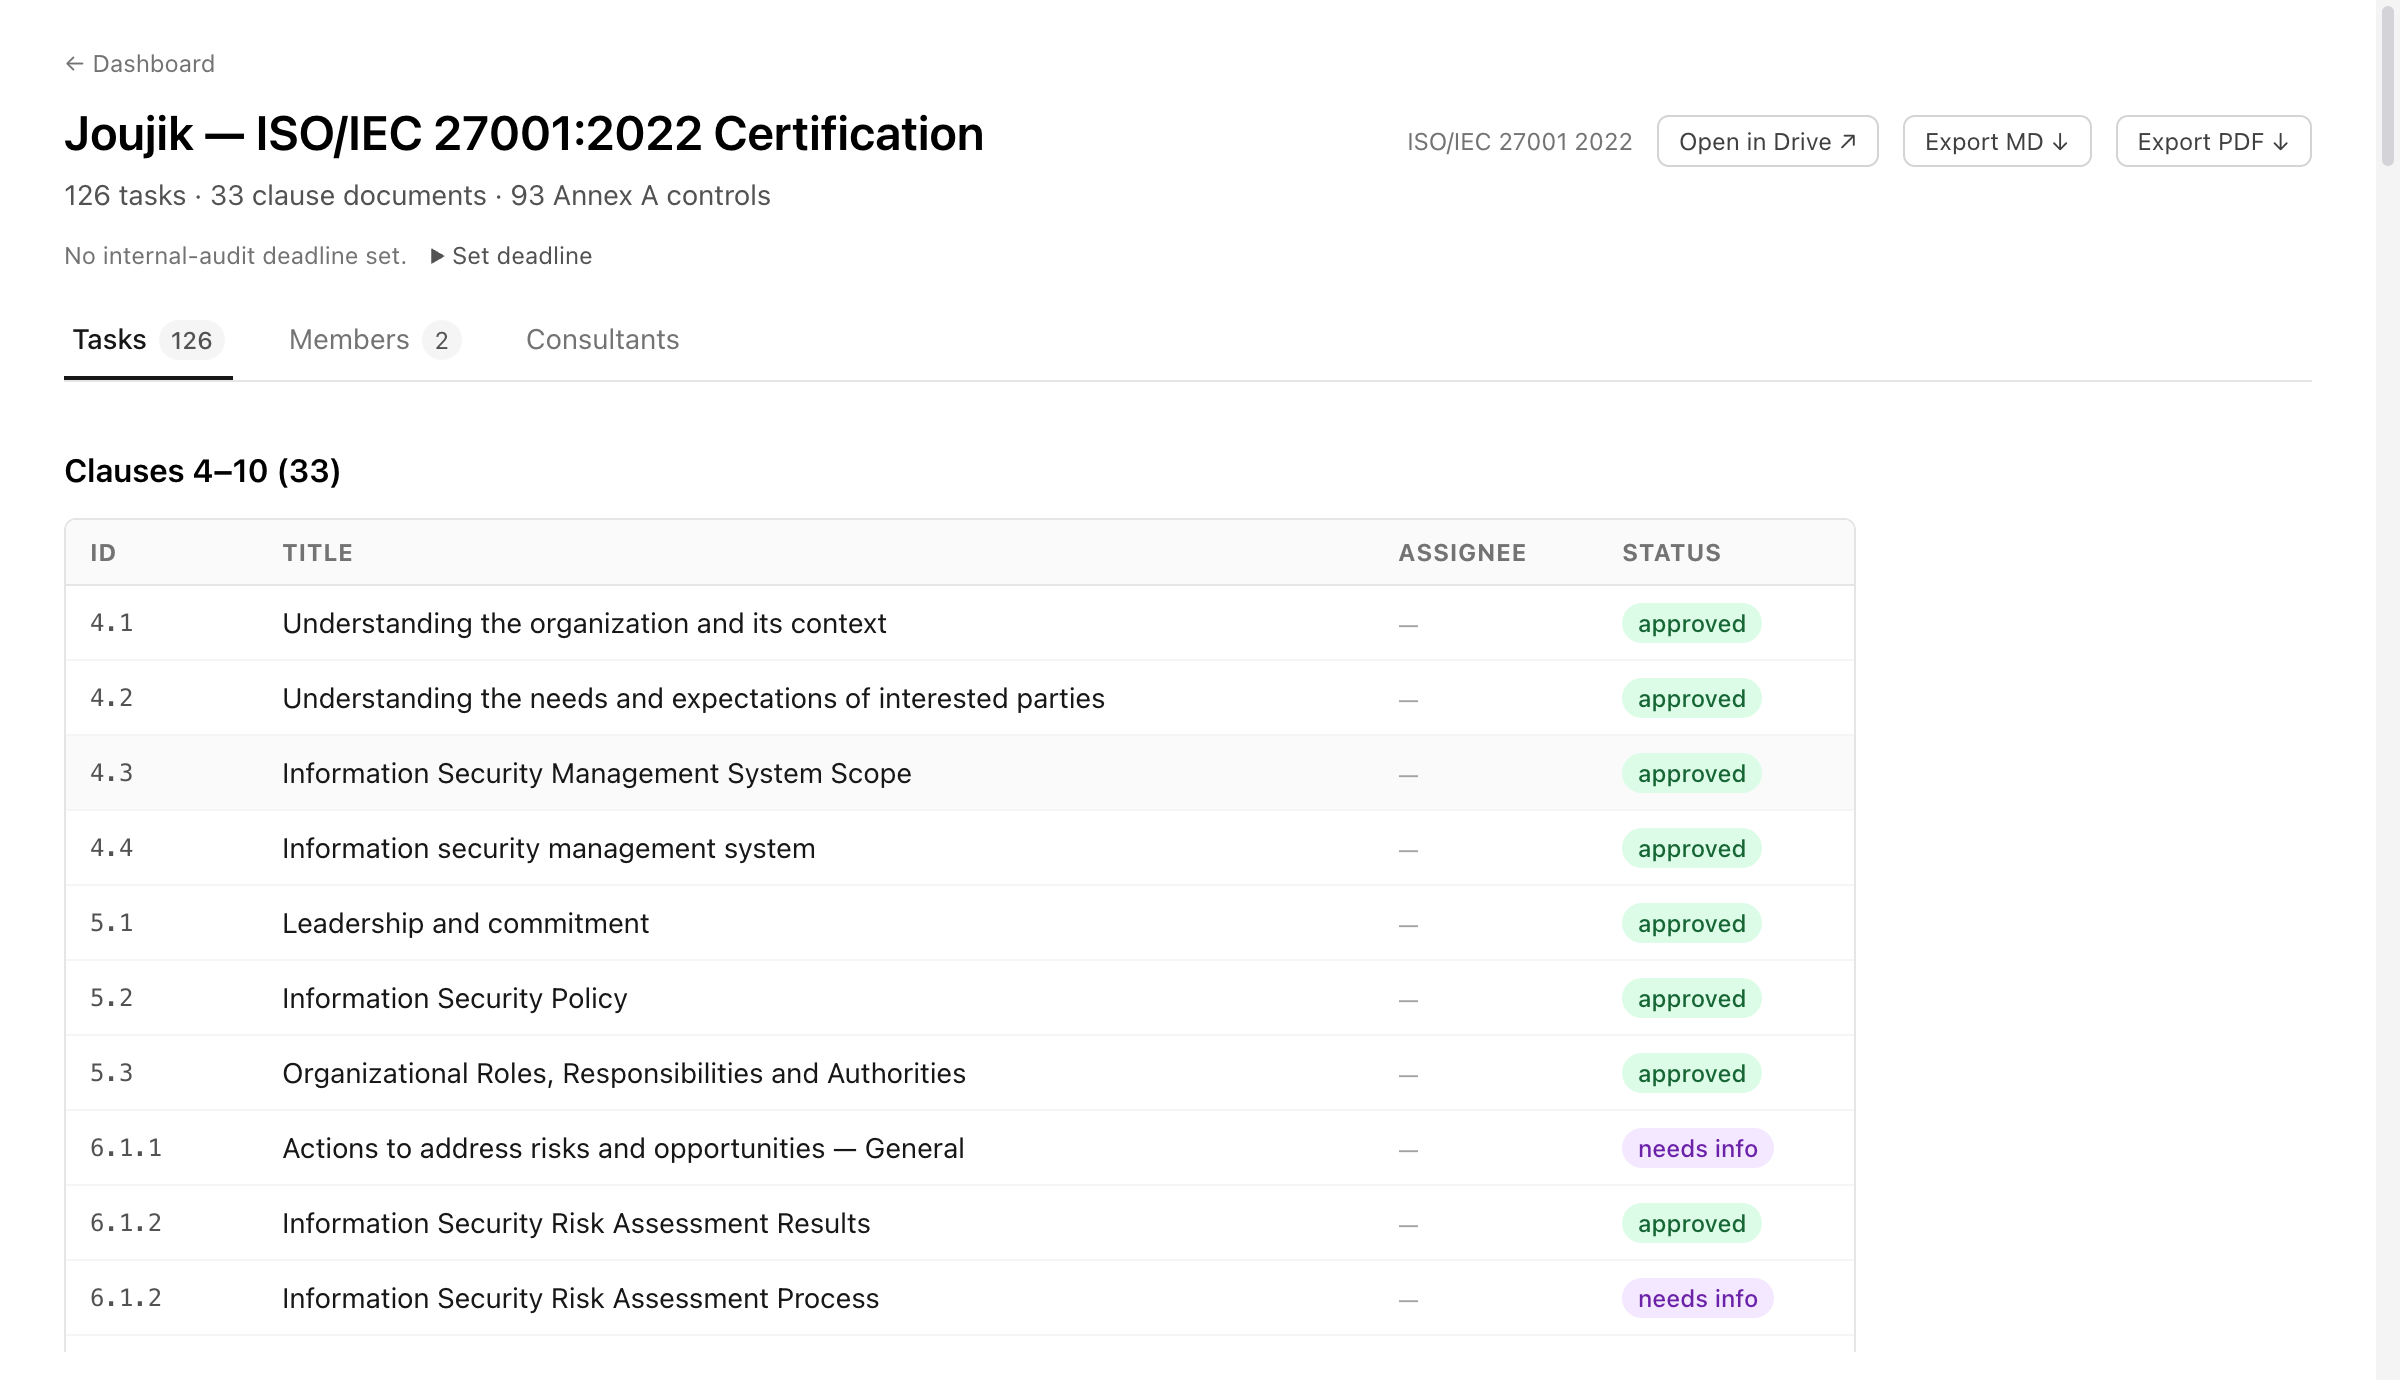
A real audit, end to end.
93 Annex A controls + clauses 4–10 · 94 comply · 21 OFI · 11 non-conformity — every verdict logged.
Every file lives in your Drive.
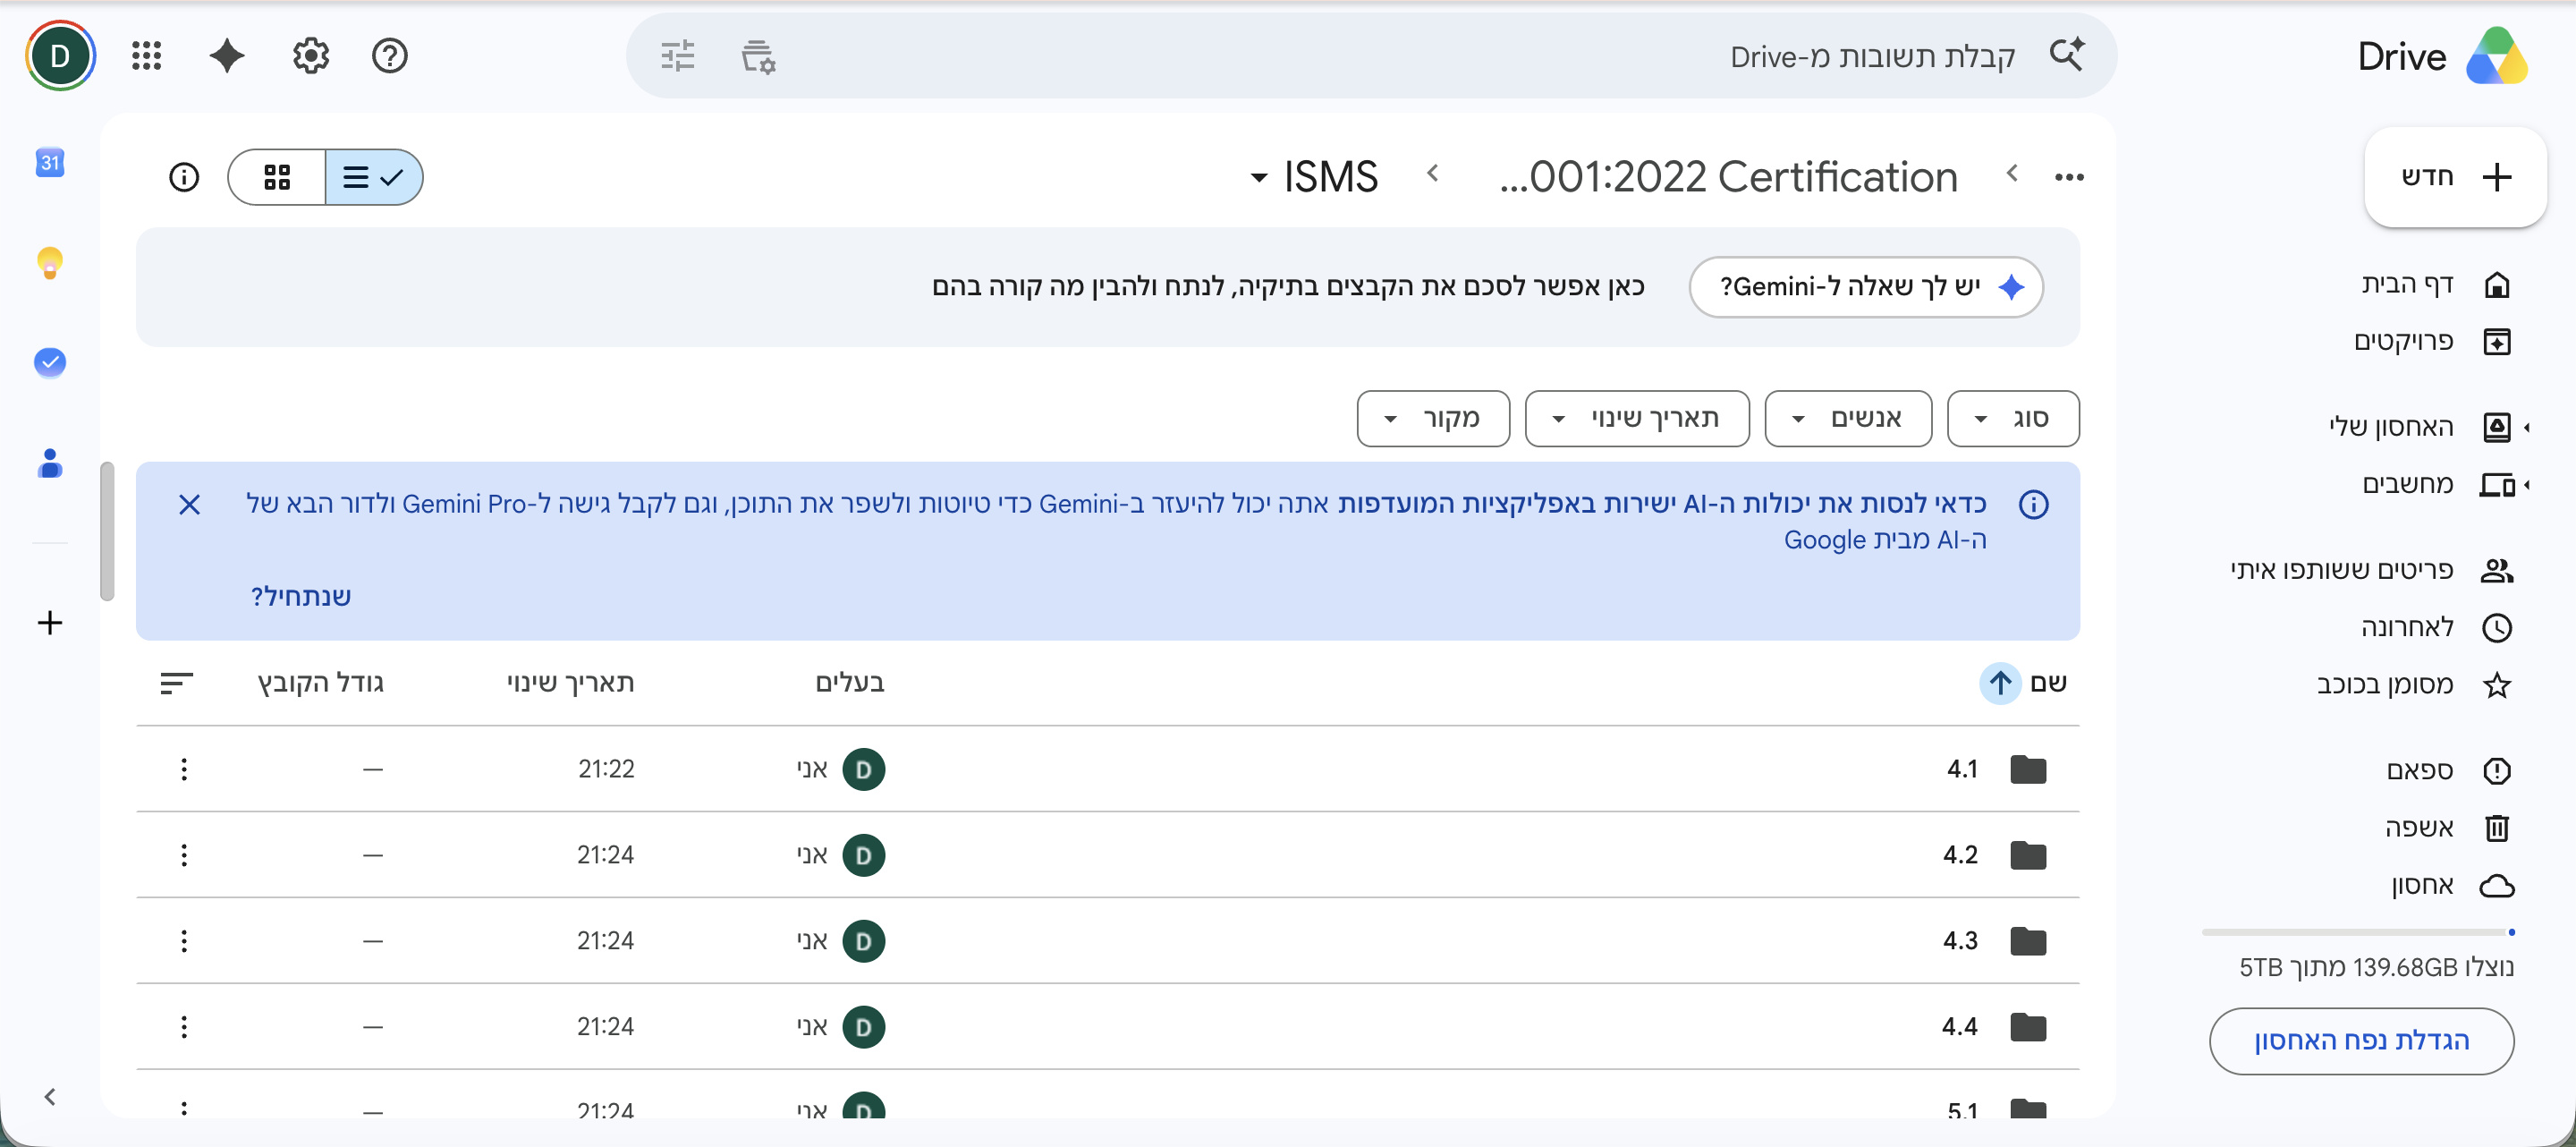
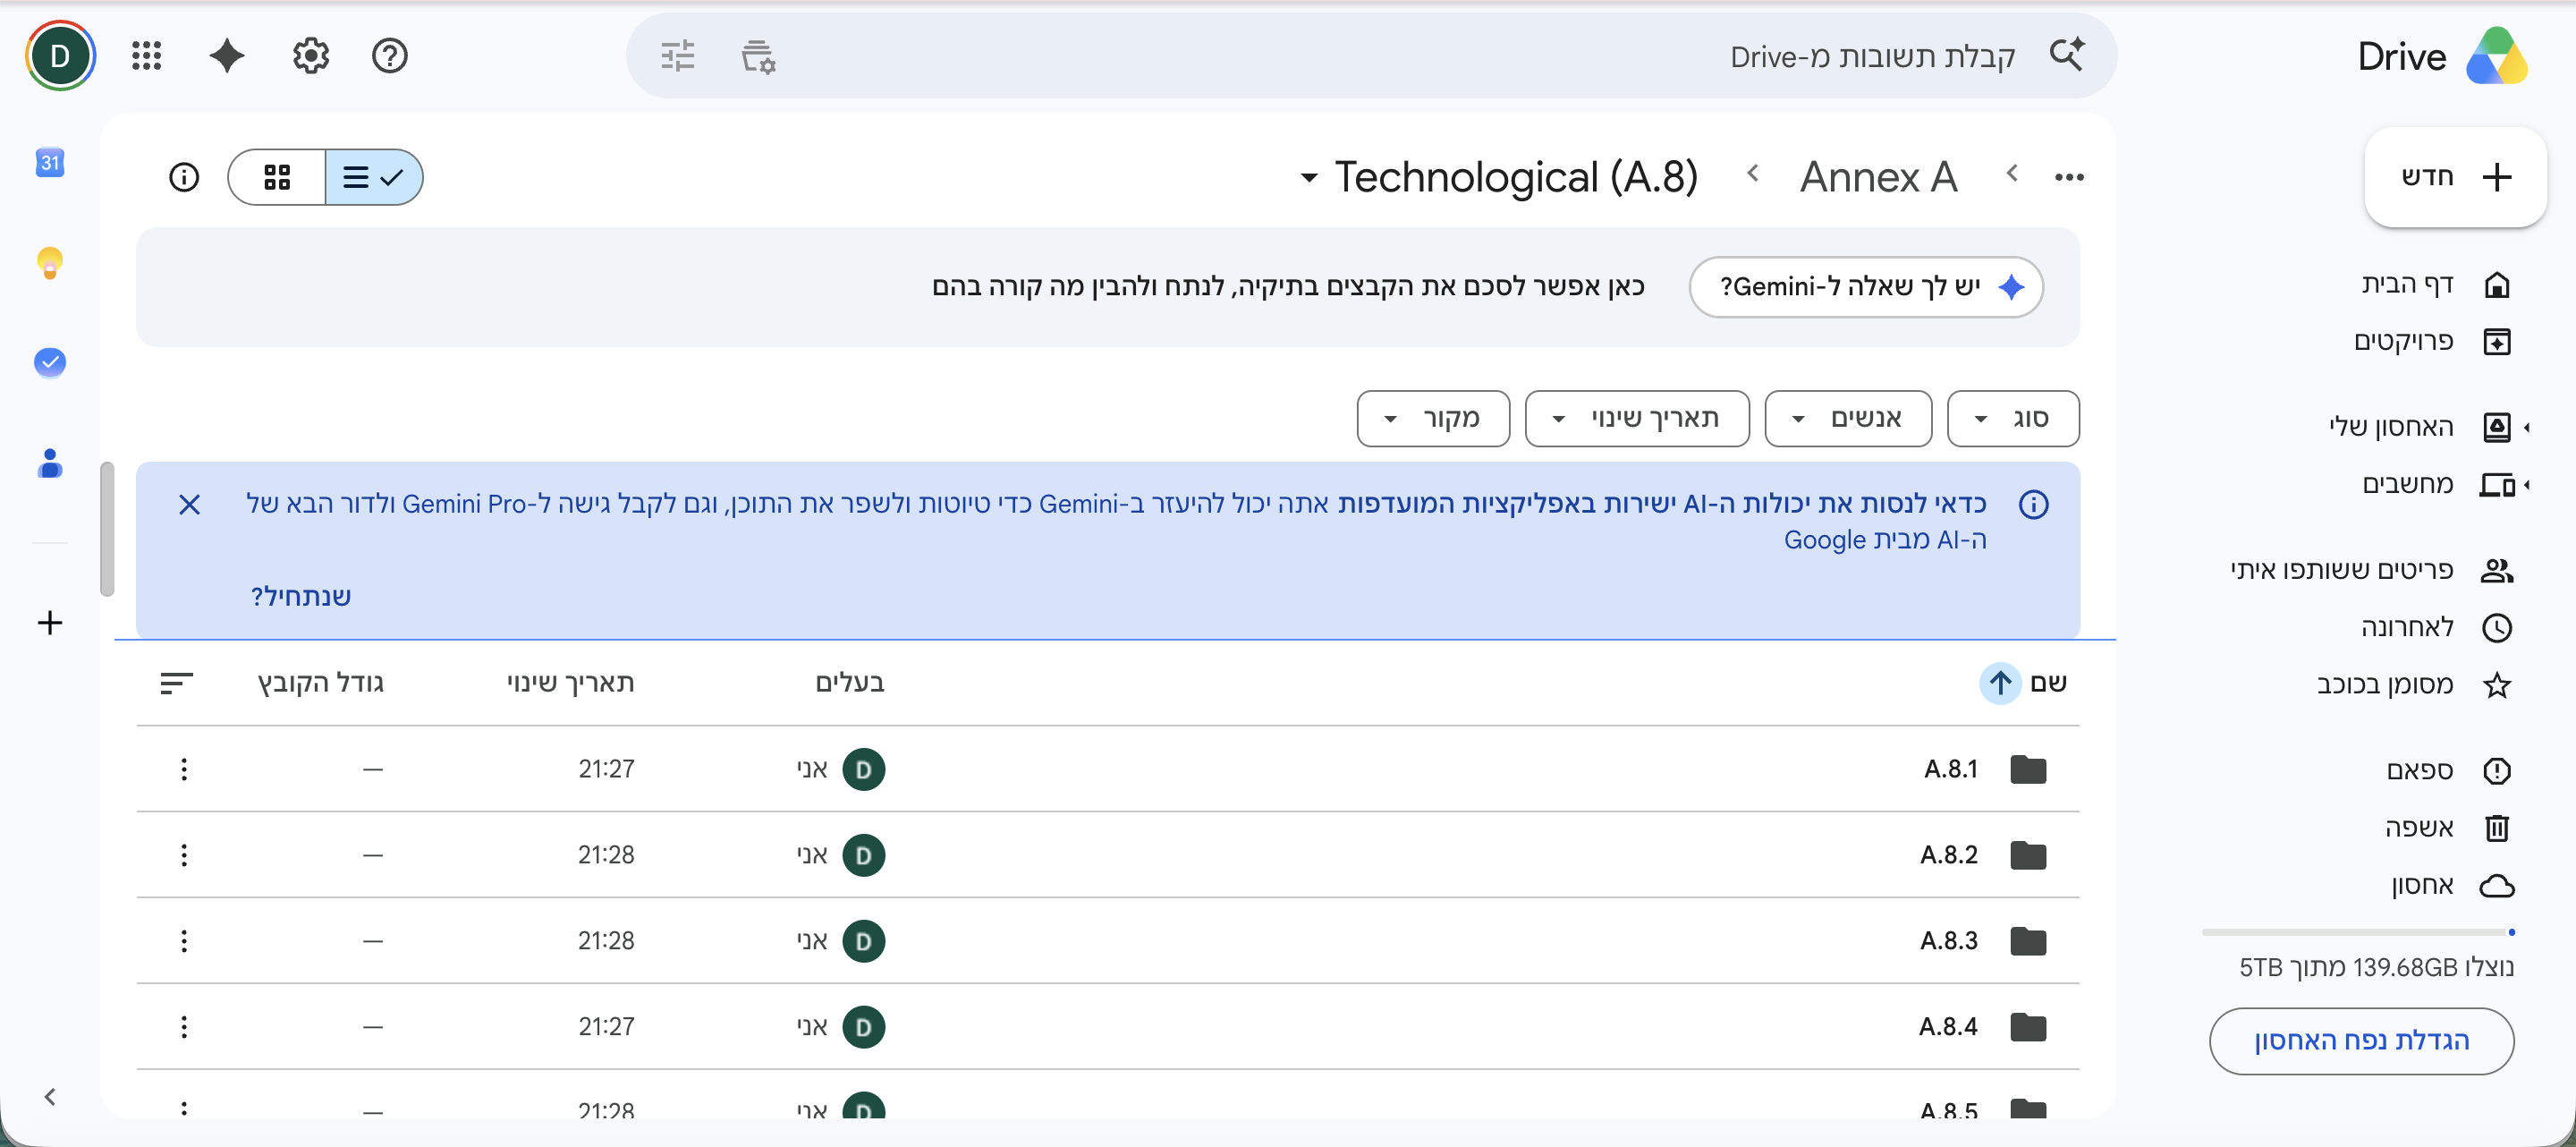
The app provisions a clean ISMS/ + Annex A/ tree with a folder per control —
created via Google's drive.file scope. Your evidence, your ownership, your portability.
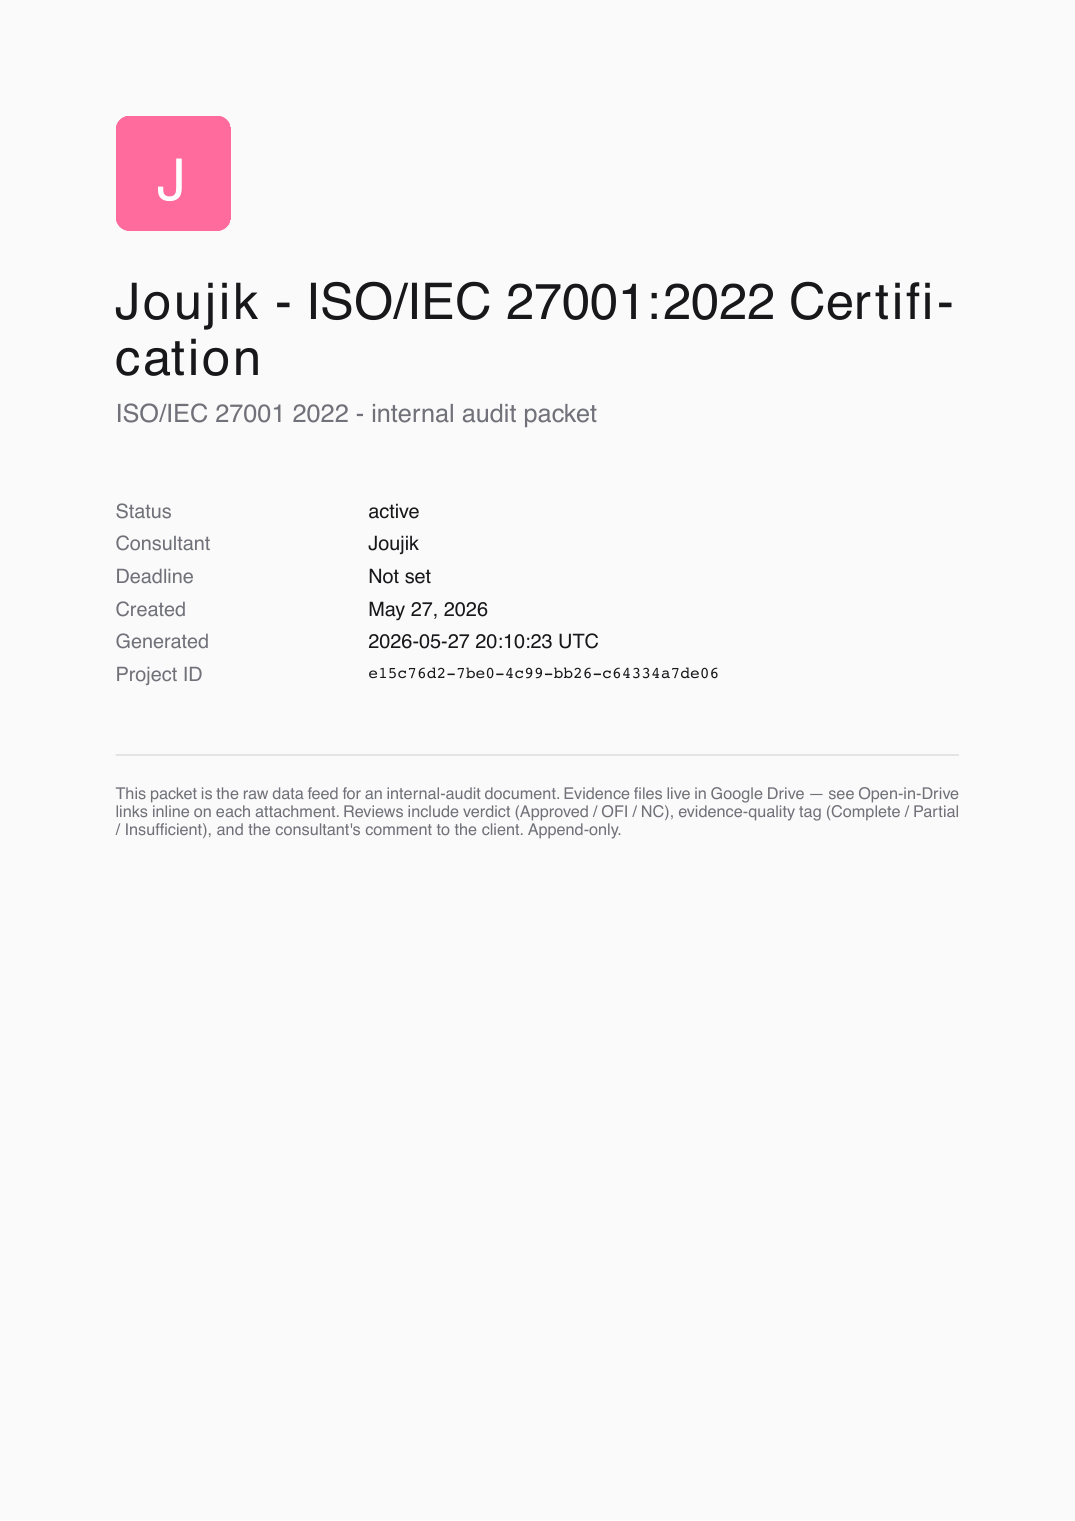
One click → a full audit packet.
Export a polished, branded PDF: cover page, the complete Statement of Applicability, and per-control evidence, verdicts & review history. Markdown & JSON exports too.
Generated from the live engagement — the 126-control ISO 27001 example shown here.
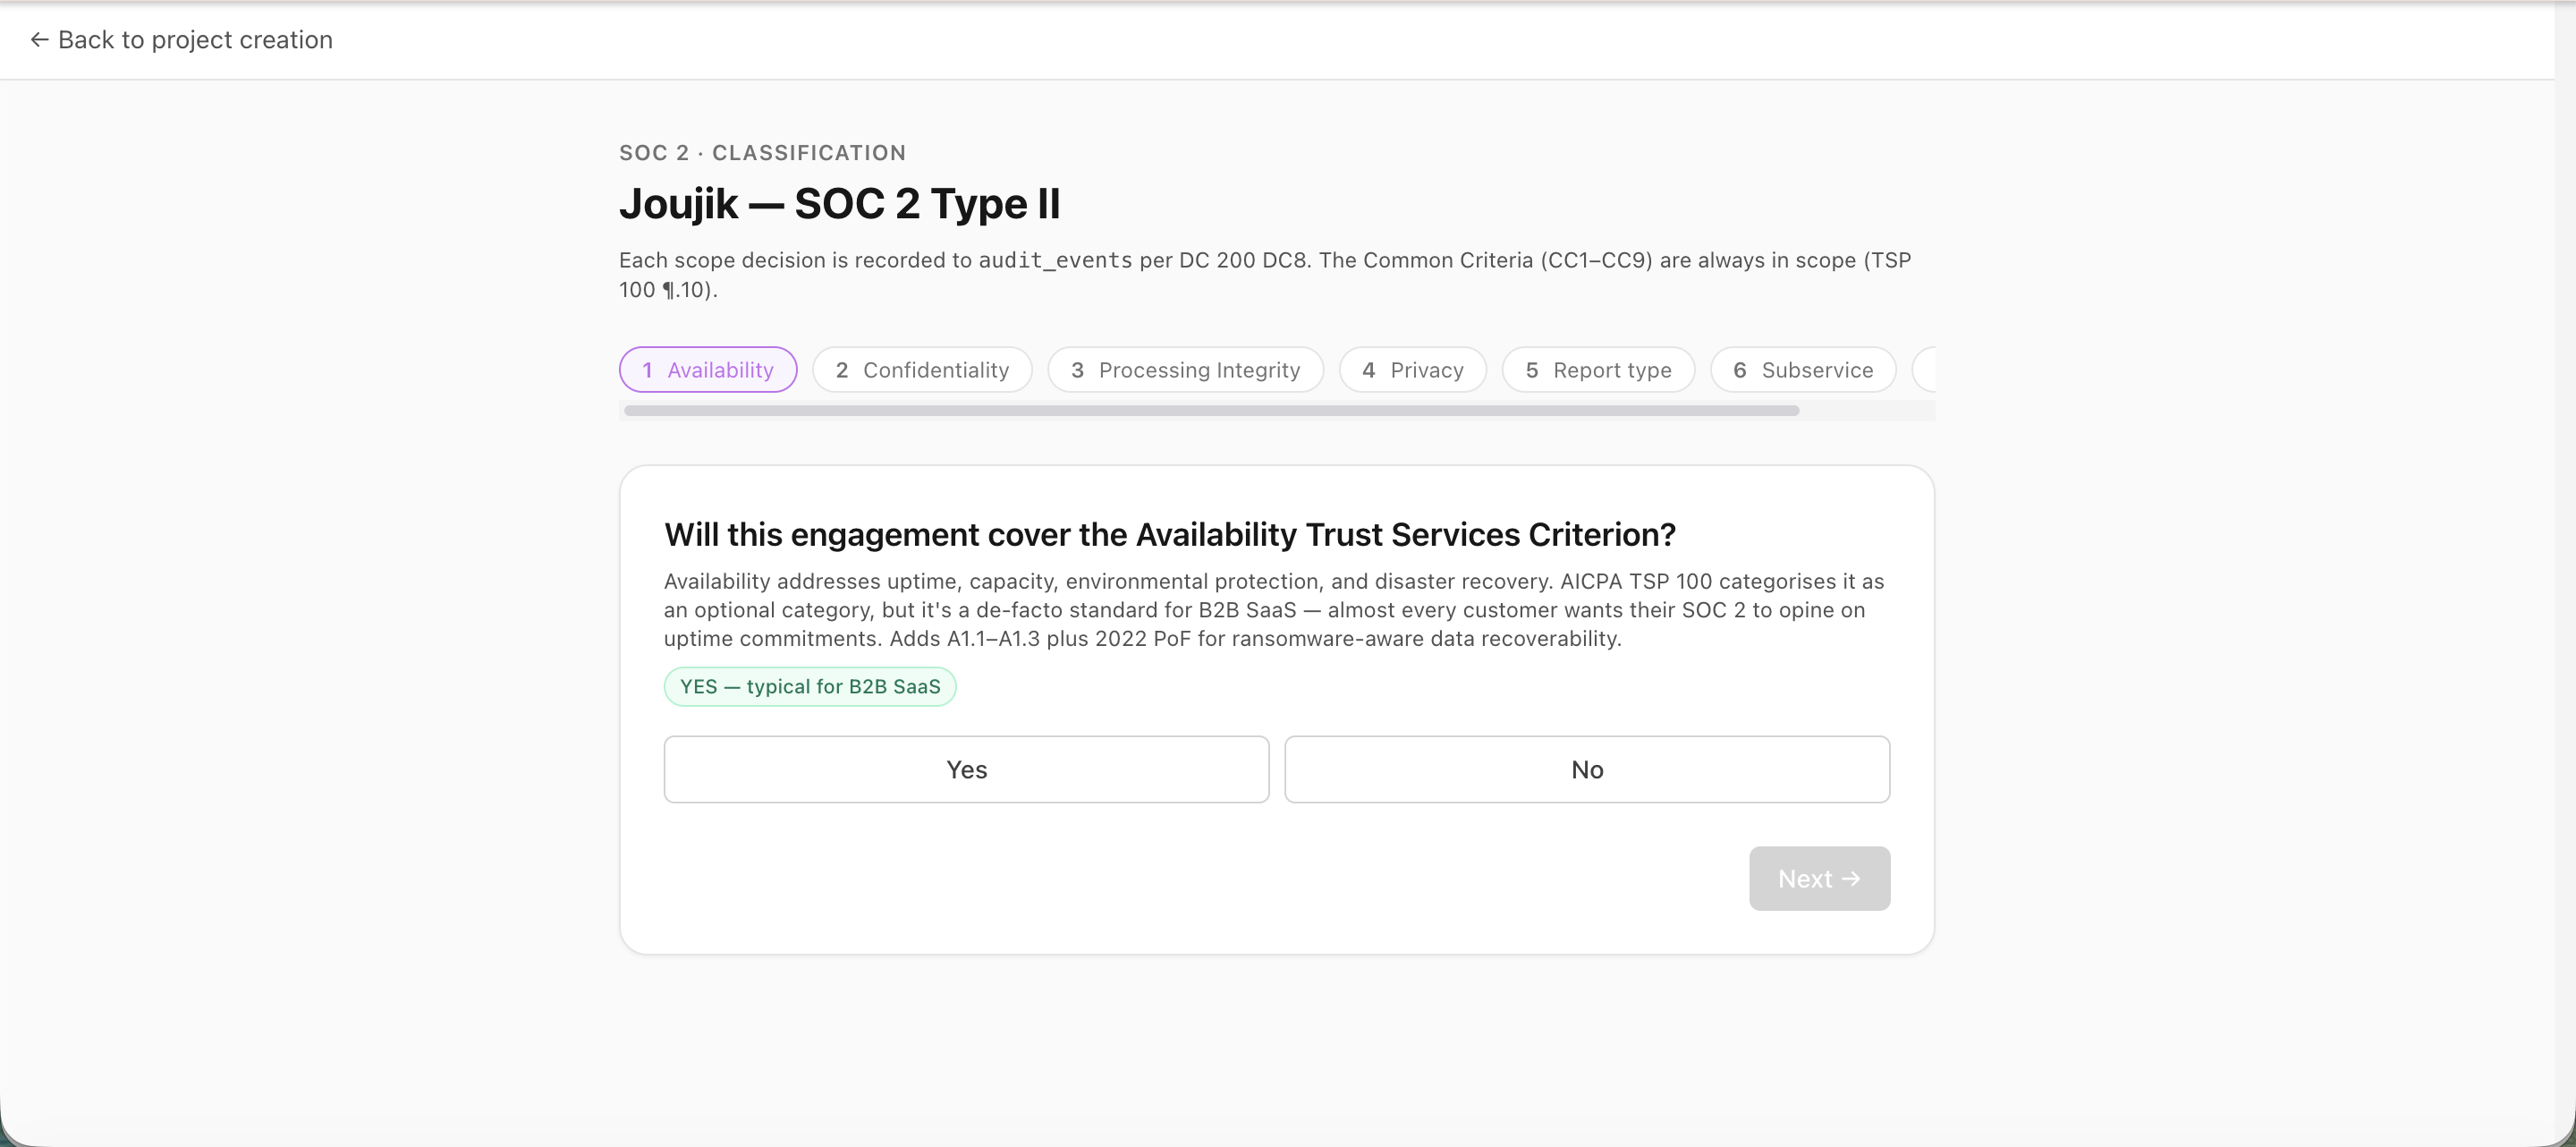
Scope the Trust Services Criteria.
A guided wizard walks Security, Availability, Confidentiality, Processing Integrity & Privacy — Type I vs II, carve-out vs inclusive — each decision cites the AICPA TSP and is logged.
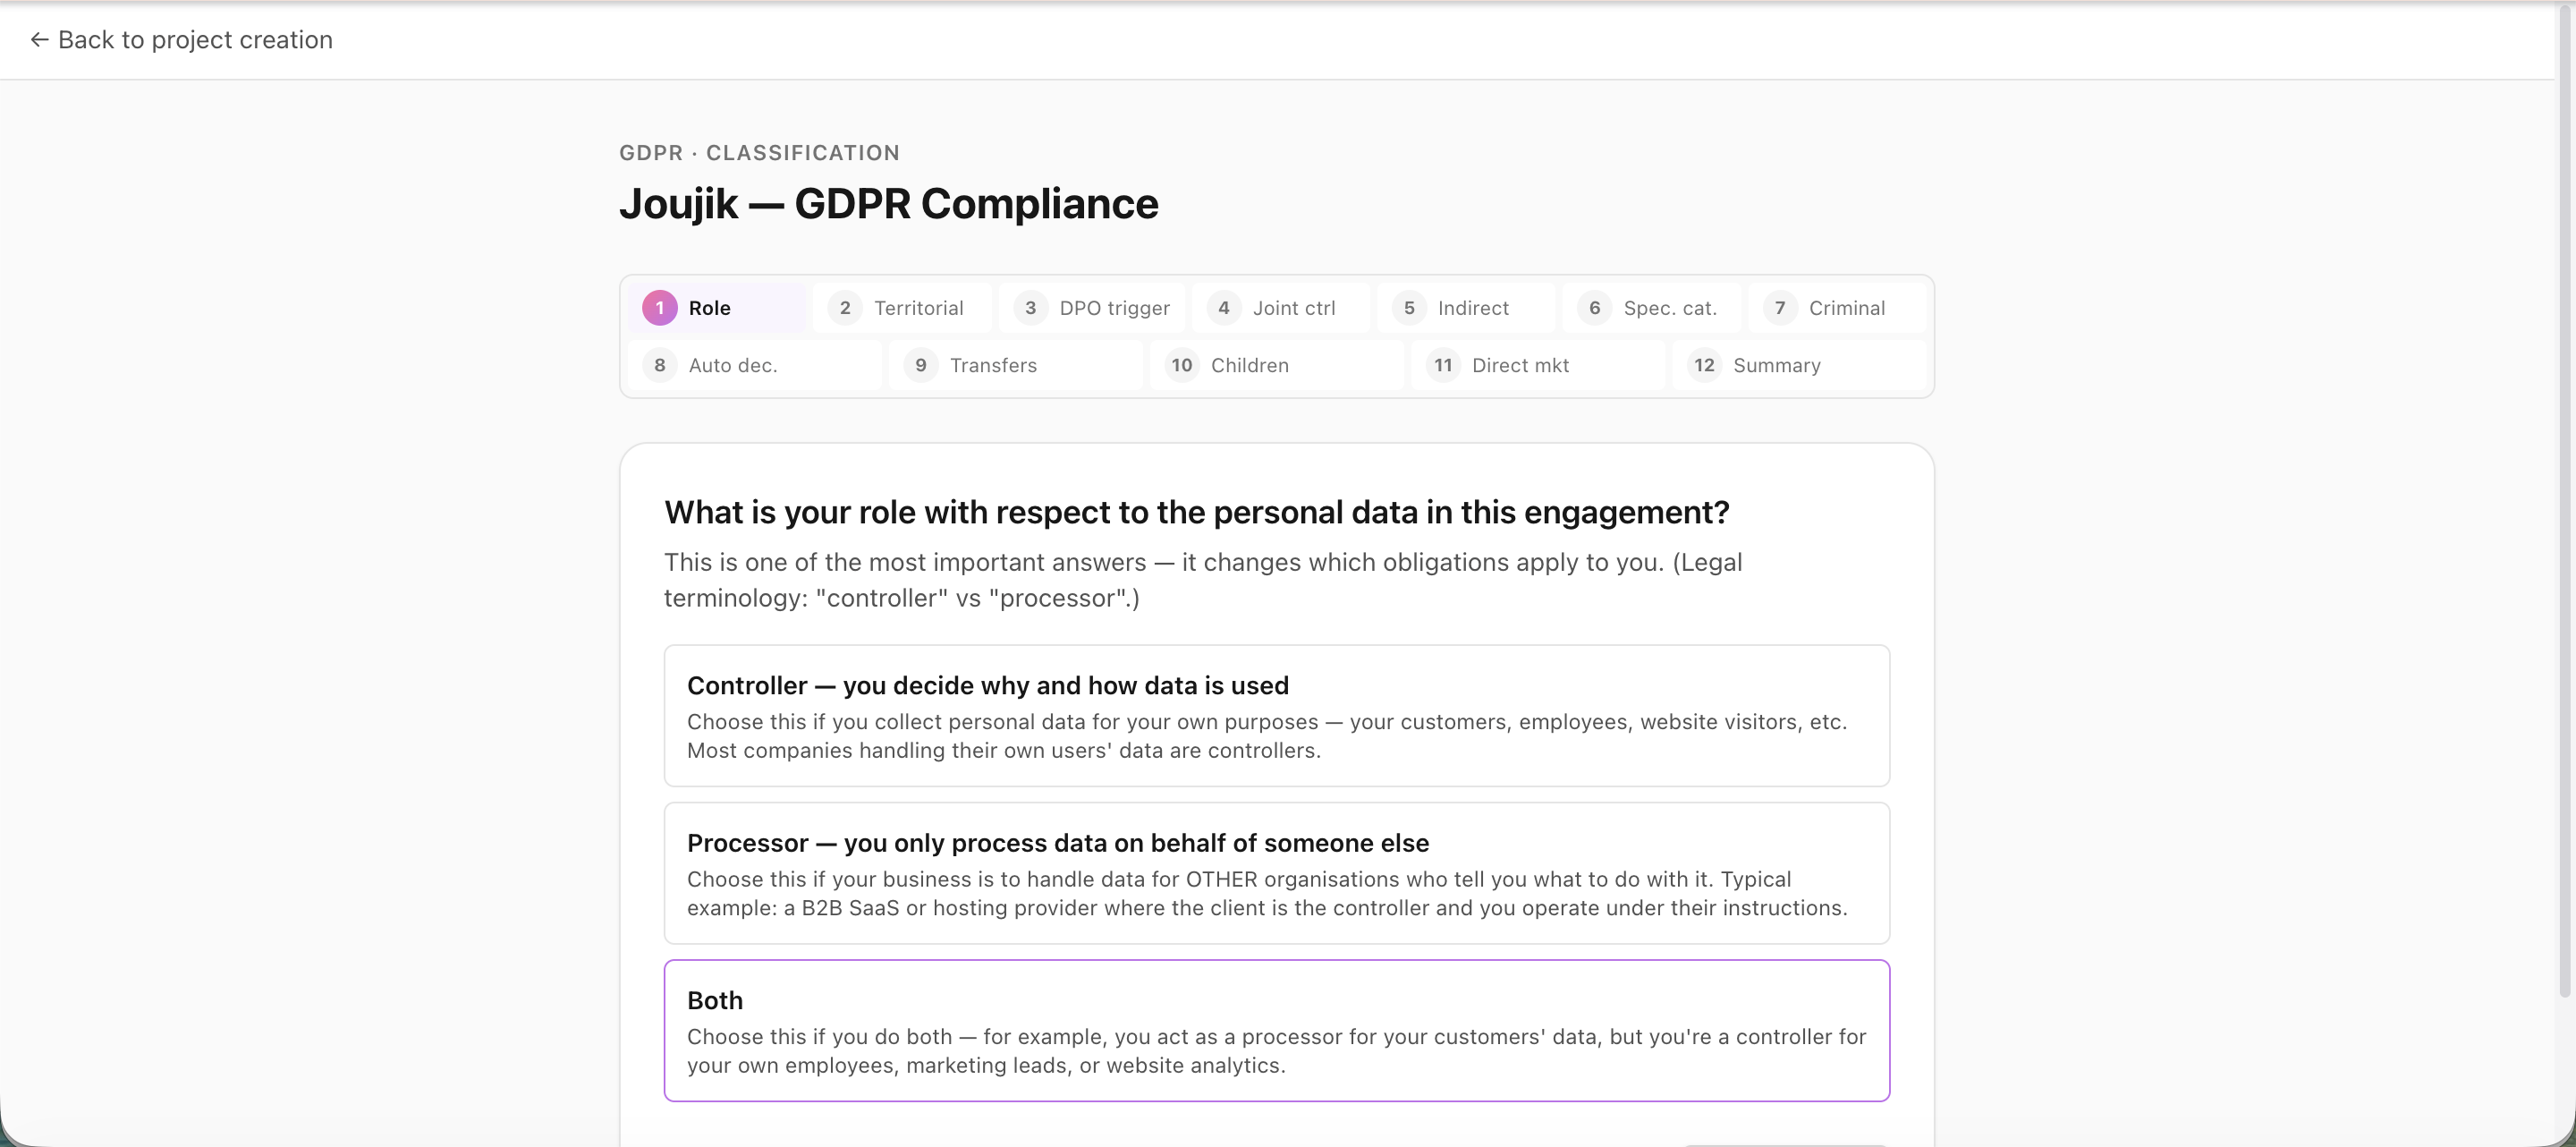
Controller or processor?
A 12-step classification — role, territorial scope, DPO trigger, transfers, special categories — with the exact legal basis (Art. 3(2), Art. 27…) cited at every turn.
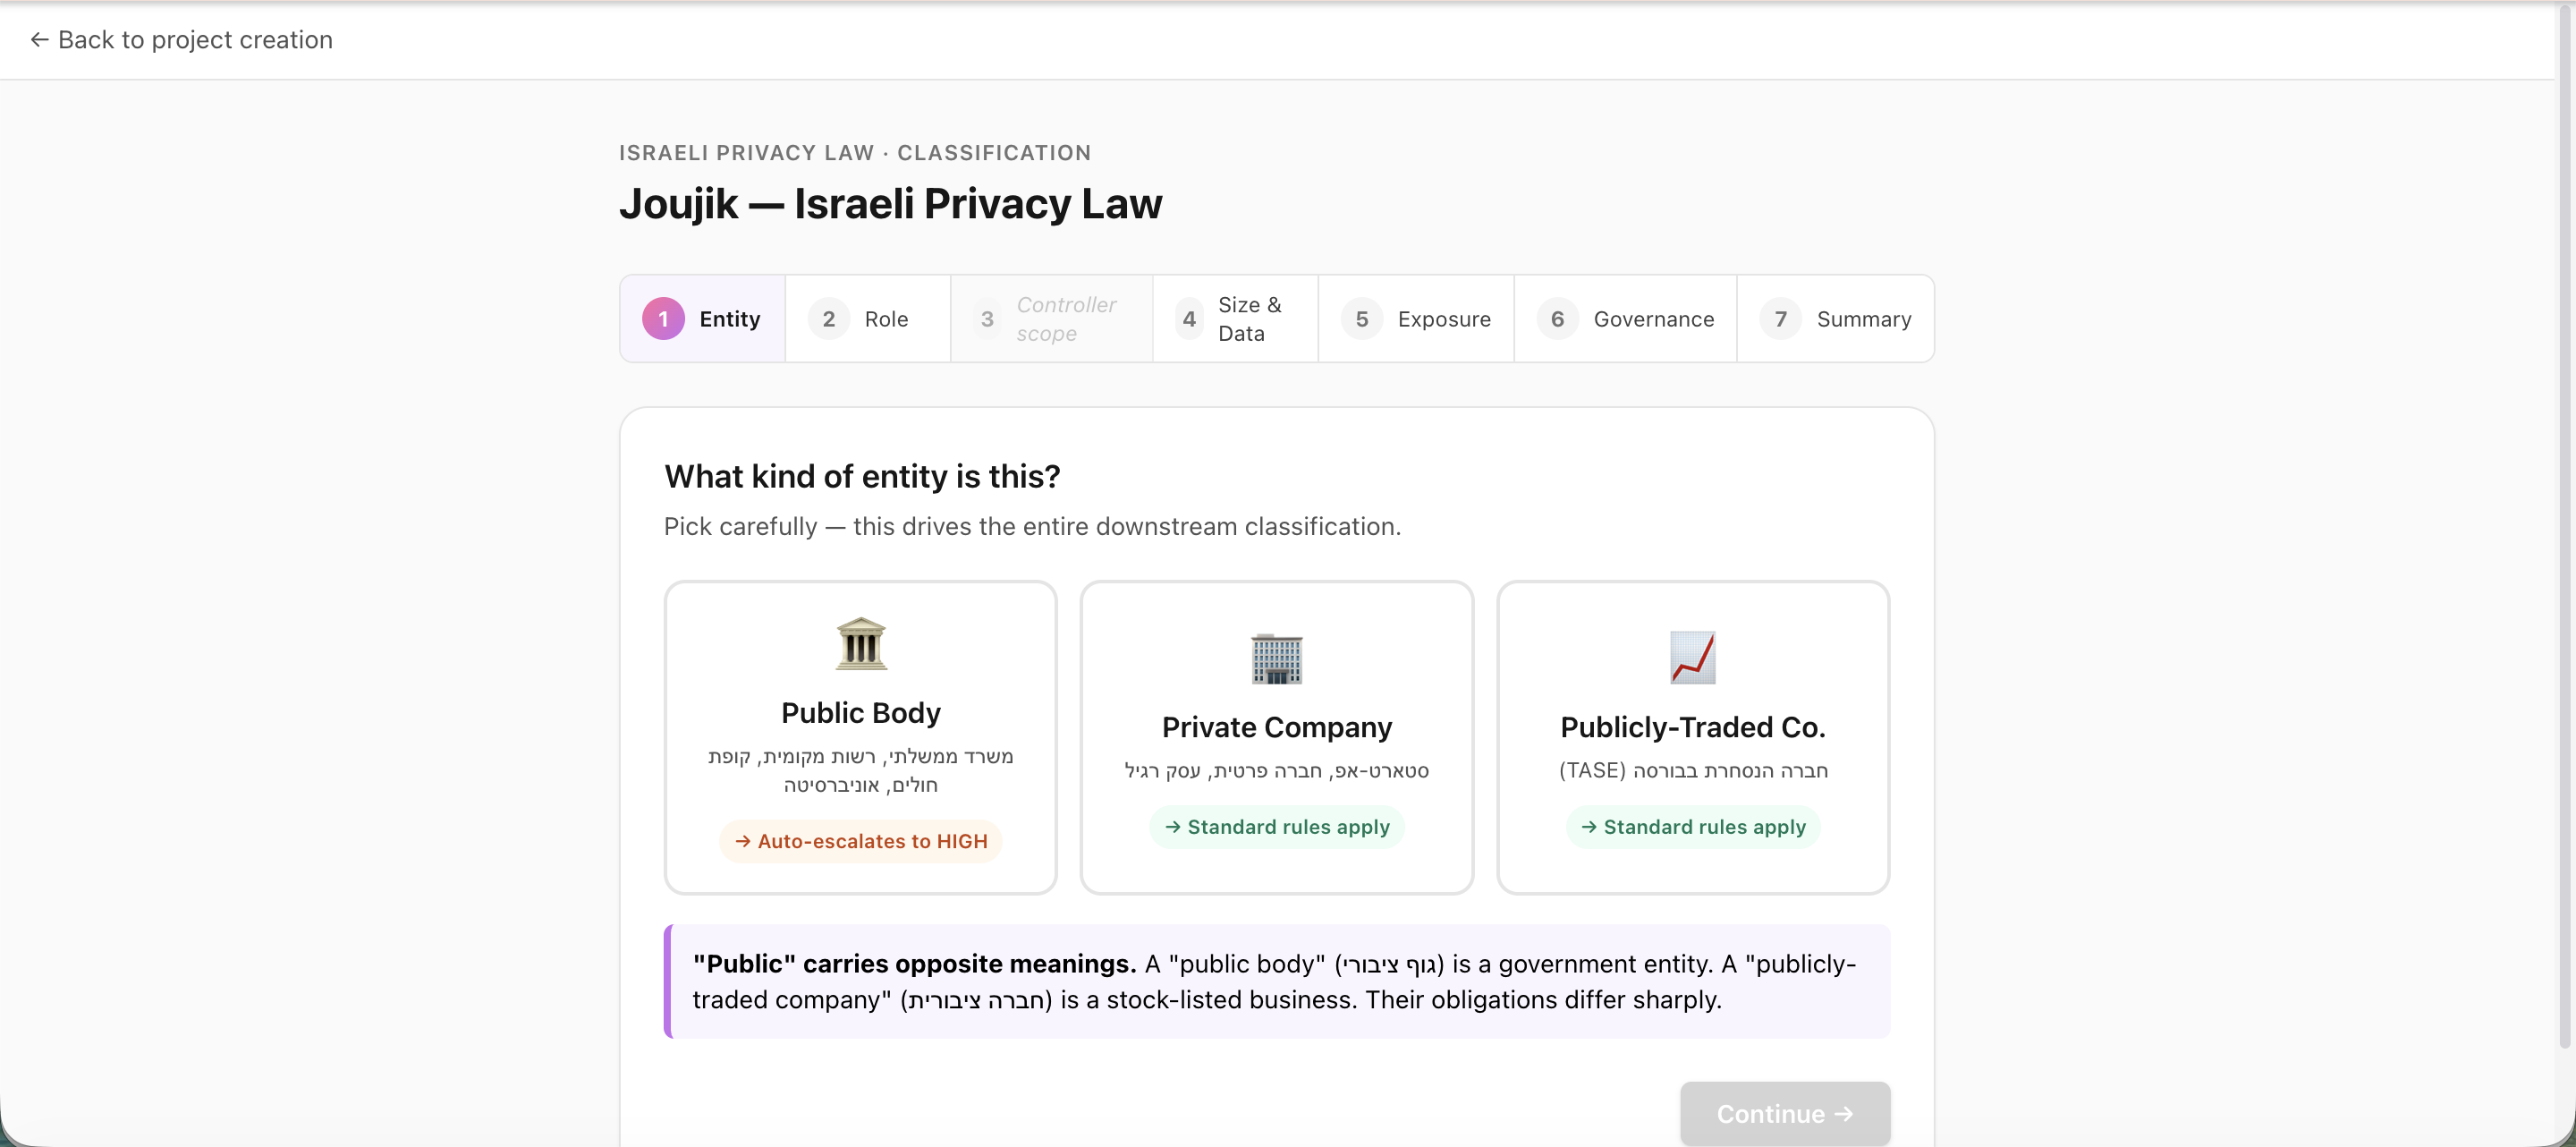
Bilingual, and it does the math.
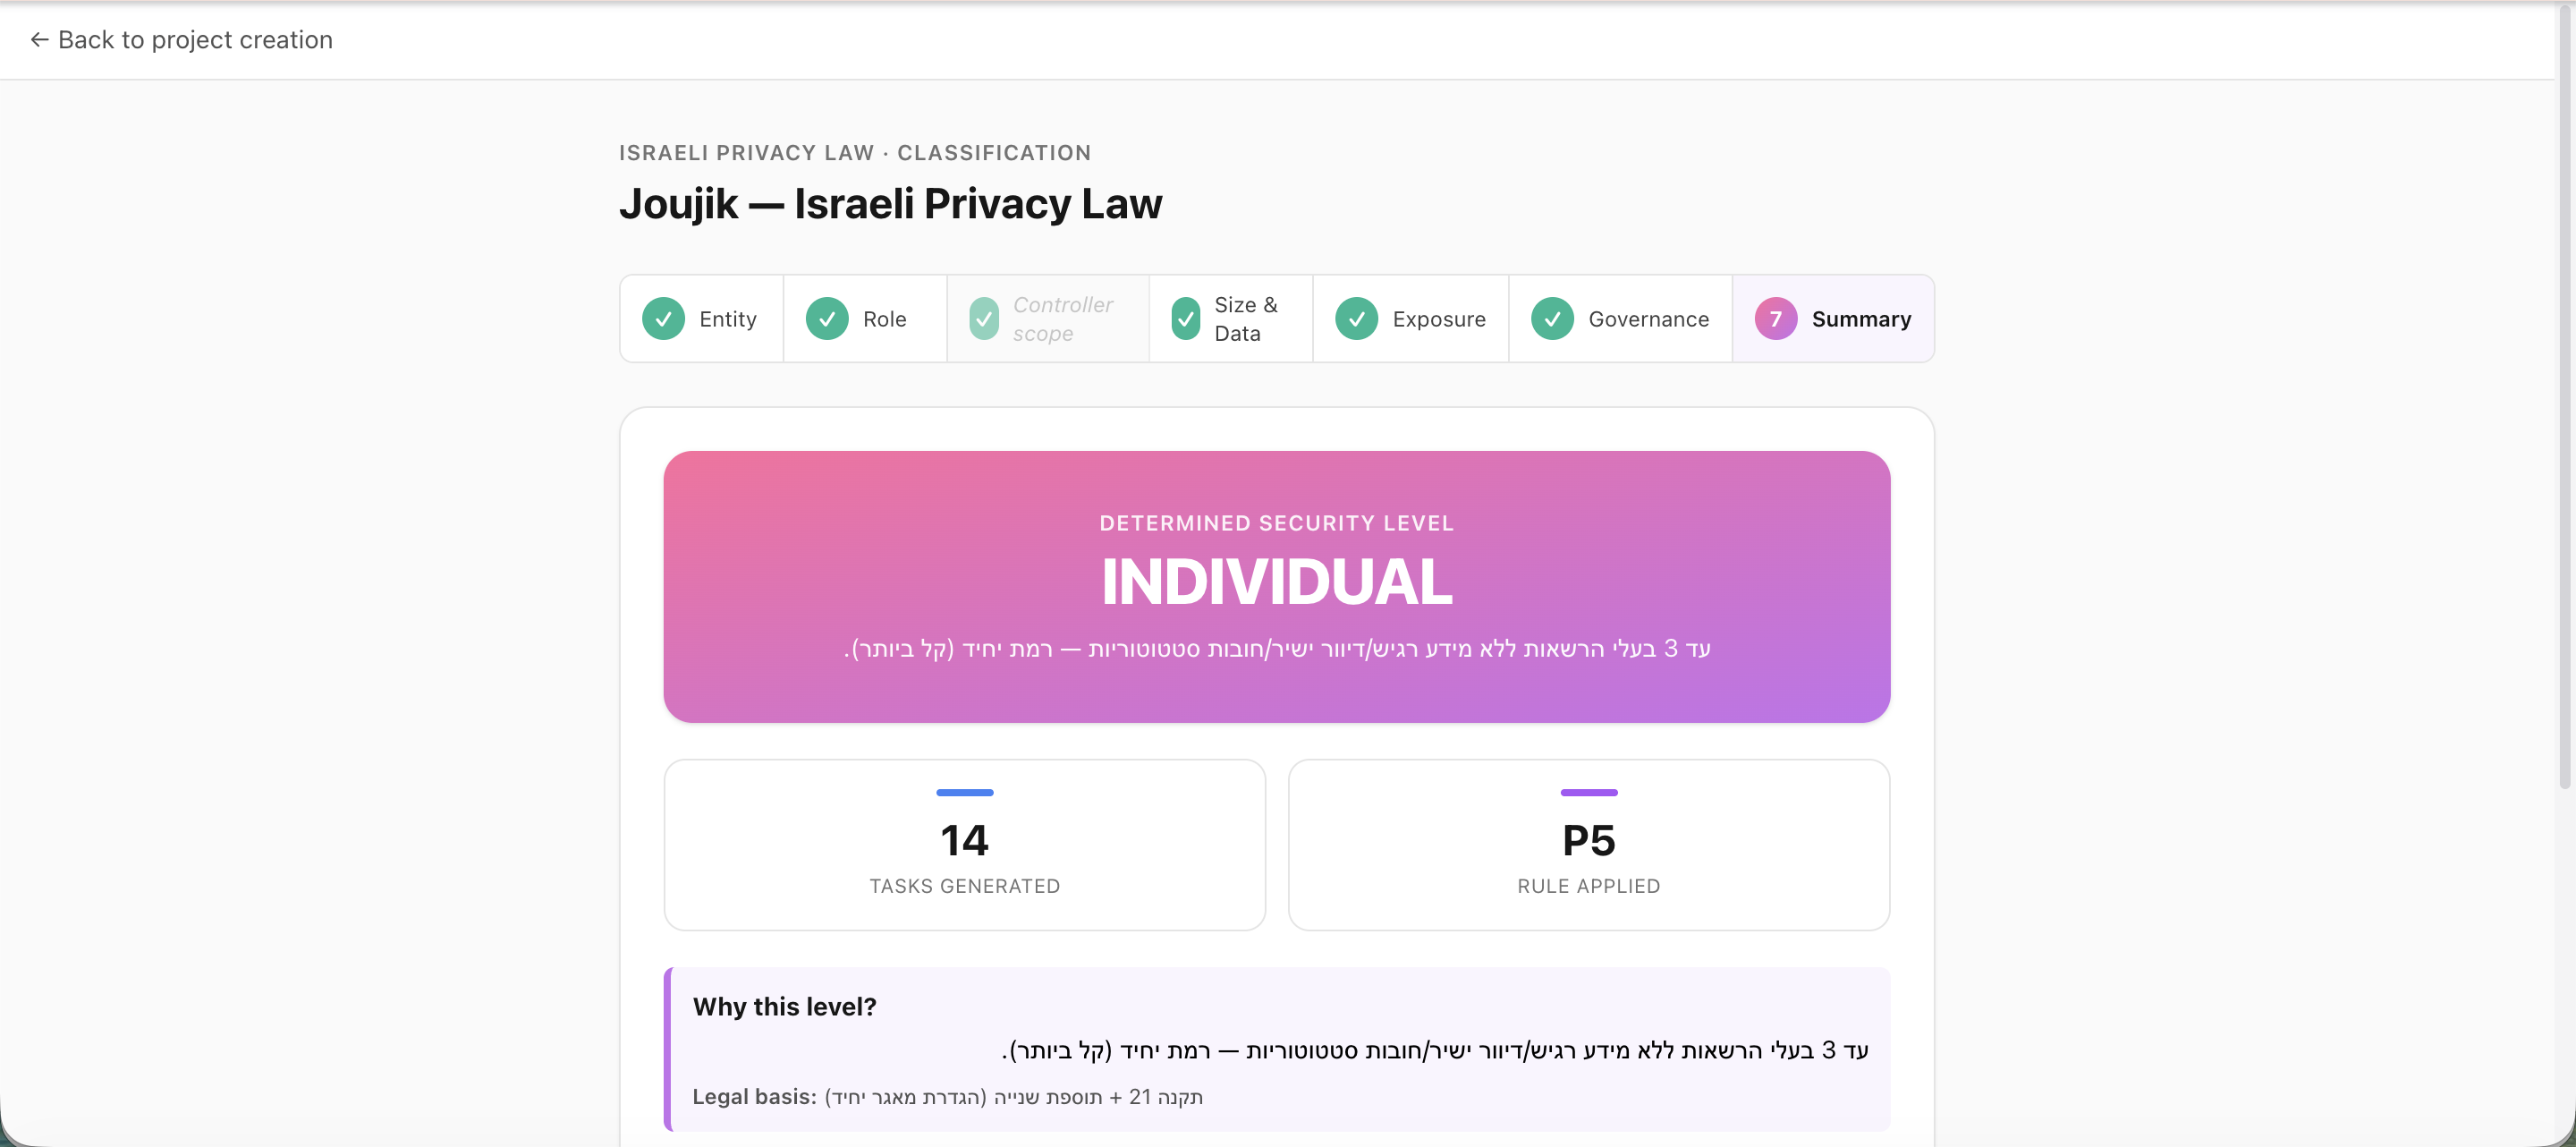
A 7-step Hebrew/English wizard classifies the entity & database, then auto-derives the security level (תקנה 21) and generates exactly the tasks that apply.
Collect once, satisfy many.
1,360 authoritative control mappings — ISO's own Annex D/E tables and AICPA sources — connect the eight frameworks. Upload evidence to one control, hit "Check crosswalk", and it's offered to the equivalent controls everywhere: one Drive file, many references, never copied.
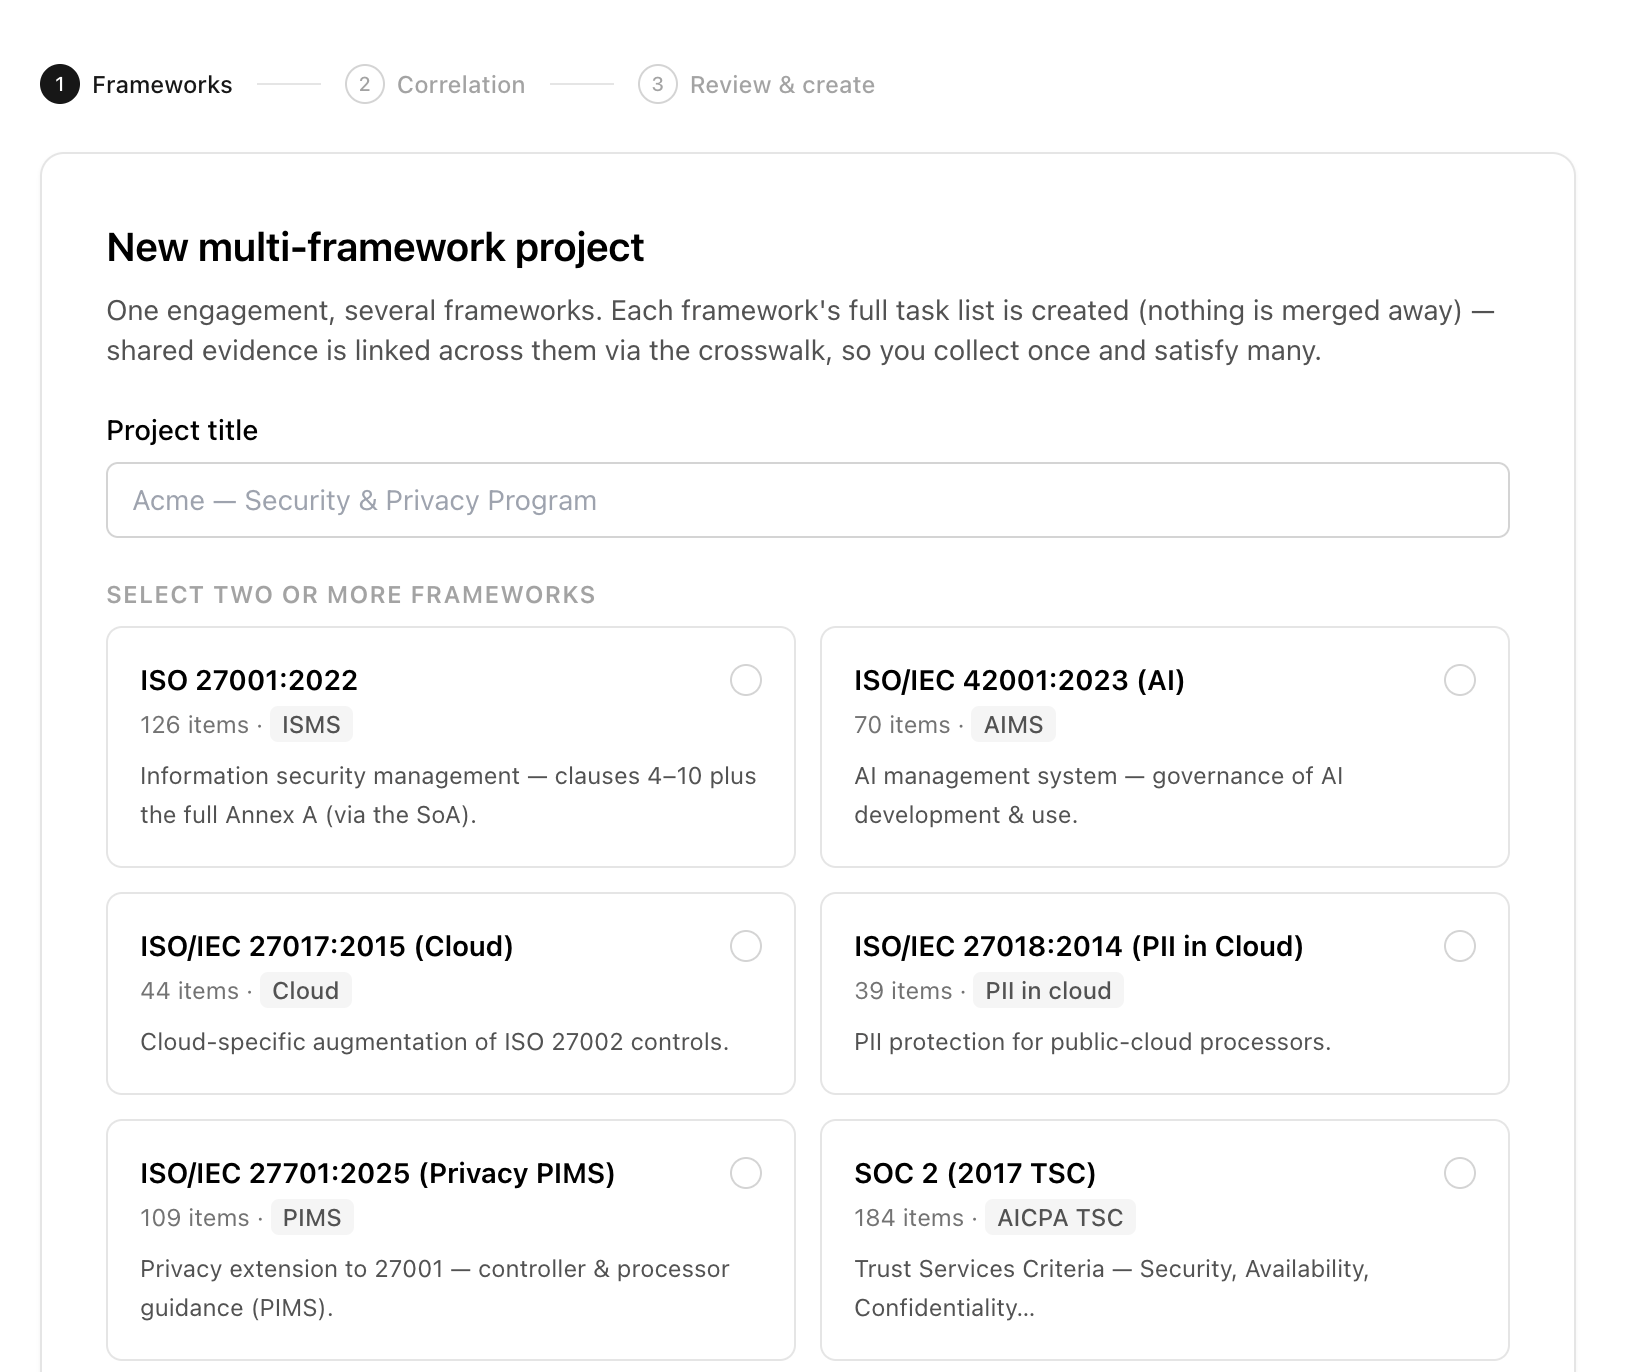
One engagement, several frameworks — a correlation preview shows the shared-evidence saving before you create it.